PRODUCTS

Cyber Security Elements by NSS

News

15

Jan

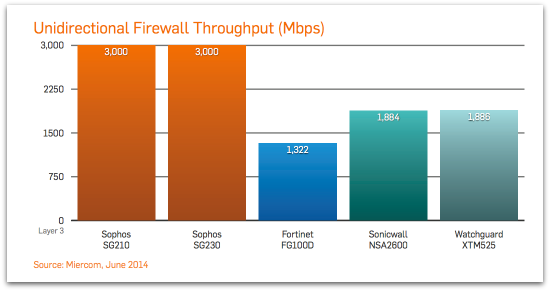
Independent test vendor Miercom has done rigorous testing of the Sophos SG Series alongside comparative appliances from other vendors. We shared some data points from Miercom earlier this year which looked very good indeed. Now Miercom has made available more results – and I don’t think you will be disappointed.

The report includes measurement of throughput for Firewall, Firewall + Application Control and Firewall + IPS (Intrusion Prevention System). Miercom also looked at how many new TCP connections can be established per second by each device.

In the firewall test, the SG appliances were so fast they didn’t come anywhere near their limits and allowed traffic to flow freely at the 3Gbps maximum.

Miercom had to install an extra port module with more ports and run traffic in both directions in order to reach the limit.

 miercom-performance-report

You can read the original article, here.
15

Jan

Once Microsoft officially ends support for XP on Patch Tuesday in April (the last security update for XP), there will be no new security updates, non-security fixes, assisted support options, or online technical content updates from Microsoft.

That means that XP users, even those with anti-malware protection from Microsoft or security vendors, will face significantly higher security risks after the end of support. As Microsoft said in its announcement, “Our research shows that the effectiveness of anti-malware solutions on out-of-support operating systems is limited.”

To ease the burden of upgrading, Sophos will officially support Windows XP Service Packs 2 and 3 until at least September 30, 2015; and Windows Server 2003 until at least January 31, 2017. See our support knowledgebase for a complete platform support list.


Upgrading to newer Windows operating systems is causing plenty of problems for specialized systems, including for point-of-sale (POS) registers, medical devices, and even ATMs. For those using “embedded” versions of XP on specialized equipment, we recommend isolating these machines and restricting access to non-essential functions using application control available in next-gen firewalls.

In most cases, however, it’s time to upgrade. As Naked Security expert Paul Ducklin writes, Microsoft’s extended anti-malware support doesn’t really change much. “Windows XP will still officially fall off the edge of the world in April 2014 when Microsoft ends support,” Paul writes.

You can read the original article here.

15

Jan

Spammers versus spam senders

There’s a big difference, because spammers generally don’t send their own spam in bulk any more. That hasn’t worked for a decade or so, because if you send 10,000,000 unwanted emails as fast as you can from the same server, or even the same data centre, you make an easily-identified target. So 1,000,000 of the messages might get loose before either the data centre (if it cares, and reputable ones most definitely do) or the majority of your recipients, or both, say, “No more!” Not only are you blocked from sending the remaining 9,000,000 emails from your truncated campaign, you probably can’t use those same servers again for days, weeks, months, perhaps ever.

How spam is delivered

Enter the botnet, or robot network. That’s an unwitting collection of surreptitously co-operating zombie computers – in homes, at offices, in coffee shops, at the mall, by the beach – that regularly call home for instructions to servers that the criminals control. The crooks can send each bot in the network a list of email addresses, and then command the entire botnet to start a giant spam campaign. Using bots, those 10,000,000 spams can be sent, say, in 10,000 batches of 1000 emails at a time, presenting a much less obvious pattern to those who defend against spam. (And sticking those 10,000 bot-infected users with the cost of the bandwidth, if you don’t mind.)

Why spam matters

I used the words “unwitting” and “surreptitious” above because, although some users may knowingly participate, the majority of botnet spam senders don’t even realise they’re doing it. That’s why we publish the SPAMPIONSHIP tables: not to lay wholesale accusations of cybercriminality against entire countries, but to raise awareness of something we’ve said a number of times recently, since it’s Cyber Security Awareness Month:

If you don’t make an effort to clean up malware from your own computer, you aren’t part of the solution, you’re part of the problem.

We’re not pointing fingers here at anyone who ever made a mistake and ended up infected by malware, but we do want you to be mindful of the consequences of inaction. For as long as you fail to do anything about spambot malware on your computer, you’re actually helping the crooks to make money, and putting the rest of us, no matter how modestly, in harm’s way.

The SPAMPIONSHIP tables

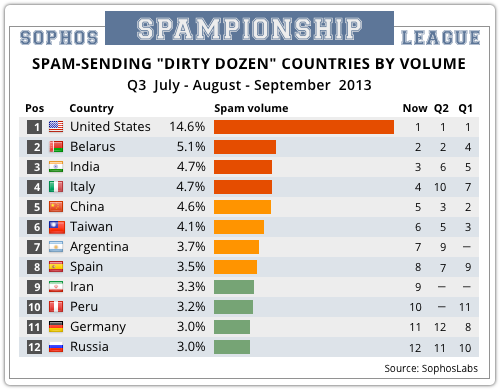
And with those firm-but-fair words behind us, here are the latest figures showing spam by volume on a country-by-country basis:

As you can see, the top of the table is surprisingly consistent, with the countries in the first five places having all been in the Dirty Dozen throughout the year. Of course, you probably expected to see India and China in the list: they each have populations exceeding 1 billion people, so it would be surprising not to see them near the top. Nor is is surprising that the USA is in the Number One spot yet again, this time sending nearly three times as much spam as second-placed Belarus. After all, the US has 30 times the population of Belarus, and internet access is much more strongly established, so you would expect a higher proportion of Americans to have their own computers and to use the internet regularly. It’s when we turn the SPAMPIONSHIP into a per capita comparison that things get interesting:

DD 2

Here, the numbers next to each country denotes the average spamminess per person compared to the USA. In other words, we divided each country’s spam total by its population, then divided every country’s spam-per-person value by the figure for America. Obviously, that makes US = 1.00, and tells us that the average computer in Belarus was eleven times more likely to send spam than if it were in the USA. Israelis, whose propensity for sending spam sneaks the Middle Eastern country into twelfth place on chart for the first time this year, were 1.8 times as likely as Americans to be spam senders. The per capita chart doesn’t do any favours to small countries, which tend to hide near the bottom of volume-only lists, even if their computers are awash with zombie malware. US neighbour The Bahamas, for example, made it to eighth spot, with double the likelihood of its computers spamming compared to the US. Luxembourg got up to fourth spot, with a spammishness 2.7 times than of the US, up from sixth in Q2 and seventh in Q3.

You can read the original article, here.
15

Jan

By offering this service, GlobalSign hopes to encourage the use of SSL in application development and the growth of security best-practices.

Through GlobalSign’s commitment to the open-source community, projects are eligible to receive one free Wildcard SSL Certificate valid for as long as the project meets minimum requirements. Open-source software projects that allow developers and the general public to freely access the source code have become very popular and are looked upon by many as leaders in the industry, representing an important segment of the technology community. Offering SSL Certificates will allow developers to improve the trust and security of their projects, which people around the world rely on. GlobalSign hopes this partnership can also make a difference by setting an example in how SSL is deployed today.

We are delighted to show our commitment to the open-source community by offering free SSL Certificates to these projects,” said Ryan Hurst, chief technology officer, GMO GlobalSign, Inc.We believe this effort will not only help the developers and users of open-source projects but also encourage the adoption of industry best-practices in the use of SSL.

To qualify for a free Wildcard SSL Certificate from GlobalSign, the software project must use a license approved by the Open Source Initiative. GlobalSign will also require that projects maintain secure SSL configurations. Projects can quickly and easily evaluate their SSL strength by using the GlobalSign SSL Configuration Checker, which currently checks for over 30 common problems relating to configuration and provides recommendations on how to fix them, thus making it easy to achieve a secure configuration.
Those in the open-source software community who are interested in obtaining a free Wildcard SSL Certificate from GlobalSign may enroll for it by visiting https://www.globalsign.com/ssl/ssl-open-source/.

Click here to see the original article.

15

Jan

In our recent UTM 9.2 release we accelerated our Intrusion Prevention System (IPS) – to do so we made changes to the underlying engine and worked at making our IPS smarter with new optimized default rule sets. We’ve been getting great reports from customers and partners about the speed boost they’re seeing.

But it’s not just software that can boost performance — it’s pretty obvious the hardware it runs on plays a critical role too. That’s why we’re releasing some new security gateway appliances that we’re calling our SG Series appliances.

These are the fastest appliances we’ve ever built. When we started the refresh project we would have been pleased with a 50% speed increase, and we were hoping we’d be able to double the speed. When our engineering team ran our benchmark tests the results were impressive — the new SG Series is up to four times faster than its predecessors. Now it’s all very well beating your own personal best but for us the real question was how would they fare in a race – just how do they stack up to the competition?

So we asked Miercom Labs, a respected testing house, to run tests. And the results were proof that we’ve built some appliances that will provide Sophos customers and partners with the best price/performance ratio anywhere in the market.

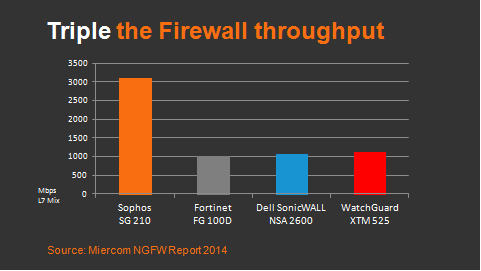
This first chart shows a comparison on firewall throughput. Now it’s important to note these results aren’t from some special, high end box targeted for thousands of users. These are from the SG 210; a mid-range model which is offered at a great price point that any business can afford.

And this performance advantage is seen not just on raw Firewall speed. The chart below shows results with Application Control enabled, a key component in next generation firewalls. As you see, our hard work paid off here as well.

miercom-app-control

And as you know Sophos has a great heritage in virus scanning and here our expertise really shows. Just look at the AV scanning numbers in the chart below.

miercom-av-proxy

This test compares AV proxy scanning which is widely known to be the most effective form of scanning because it looks at the entire file rather than taking shortcuts. But not everybody can do it “at speed,” and as you can see some don’t offer it at all.

The complete report from Miercom Labs will be published soon but as we announce the availability of the new SG Series appliances I just wanted to share some of the great results we are seeing. And as we extend the SG Series and continue to optimize our software here’s to even faster, even better protection!

You can read the original article here.

15

Jan

The Federal Communications Commission reports that mobile phone theft constitutes 30-40% of all robberies across the United States, a crime that cost US citizens $30 billion in 2012. In the Senator’s own state of California such thefts are even more prevalent, accounting for over 50% of street robberies, Los Angeles alone has seen a 12% increase in smartphone thefts over the last year. If the kill switch legislation is passed, carriers will be able to remotely send a message to any device that has been reported as either lost or stolen. That message would trigger the device to ‘brick’ itself, effectively making it useless, and a far less appealing option for would-be thieves. With a few exceptions, most phones do not offer any form of remote deactivation at this time which makes them especially appealing to thieves who can snatch and sell them on in a very short period of time. 

One manufacturer that does offer deactivation is Apple, though Gascón would like to see such a feature become the default rather than an option: “Apple should be commended for leading the way and making efforts to safeguard their customers, but it is still too early to tell how effective their solution will be. Until Activation Lock is fully opt-out, it appears many iPhone owners will not have the solution enabled. This leaves iPhone users at risk as thieves cannot distinguish between those devices that have the feature enabled and those that do not”.

Kill Switch 2

Gascón, along with New York Attorney General Eric Schneiderman, have asked mobile phone manufacturers to propose methods of curtailing the theft of smartphones. Having presented the tech companies with a June 2014 deadline, Gascón said: “I appreciate the efforts that many of the manufacturers are making, but the deadline we agreed upon is rapidly approaching and most do not have a technological solution in place. Californians continue to be victimized at an alarming rate, and this legislation will compel the industry to make the safety of their customers a priority”.

The bill will be formally introduced in January 2014.

The readers who wish to protect their Android devices in case of loss or theft can install Sophos’s free Antivirus and Security app which includes the following features:

  • Supports remote commands for Wipe, Lock, Alarm, Locate, Reset passcode and Message to finder
  • Reporting of the device location before the battery runs out
  • Notification if the SIM card is replaced

You can read the original article here.

15

Jan

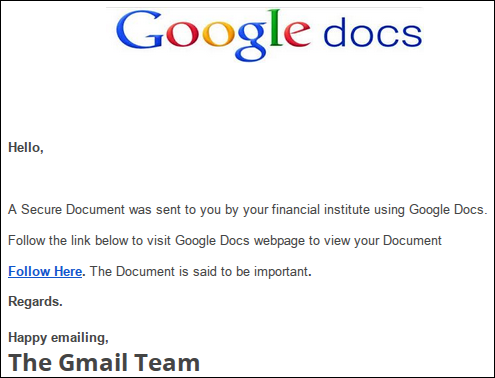
The email reads:

    Hello,
    A Secure Document was sent to you by your financial institute using Google Docs.
    Follow the link below to visit Google Docs webpage to view your Document
    Follow Here. The Document is said to be important.
    Regards.
    Happy Emailing,
    The Gmail Team

Phishing emails aren’t exactly rare, but this one caught my eye. In addition to being a somewhat plausible lure, it is an equal opportunity exploit. If you click the link you are presented with a phishing page hosted in Thailand. The page not only asks for your Google credentials, it also suggests it will accept Yahoo!, Outlook.com, Hotmail, AOL, Comcast, Verizon, 163.com or any other email account.

gdocsphish2

Of course, filling out this form can only end in tears. Your details are sent off to the compromised servers for whatever purposes these thieves desire.  You might think, “So what? My Gmail isn’t full of secrets that will destroy my nation/life/career.” You would likely be wrong, because your email is the key to unlocking much of your online identity. Forget your banking password? No worries, they will email you a password reset link. Does your company utilize cloud services? Your email account is likely key to accessing these systems. Phishing is an amazingly successful technique. Just ask the Syrian Electronic Army, who with little technical talent have been able to compromise some of the most powerful media organizations in the world. As an IT administrator, these are opportunities to educate your staff on the risks.

gdocsphish3

This might not be the most convincing of the phishes that are out there, but it is a useful tool to educate your staff. Many organizations are using Google and other cloud service providers to provide critical IT services. At first glance this could be very believable. What do I do to avoid being a victim? I create shortcuts in my browser for all sensitive services. If I need to access my email, bank or other online service, I don’t click the link; I click the favourite.

You can read the original article, here.
15

Jan

Sophos is the only IT security company to be positioned as a Leader across three critical security areas: Unified Threat Management (UTM), Mobile Data Protection and Endpoint Protection Platforms. “We believe it is a privilege to receive recognition from Gartner. The momentum in our UTM business is truly exciting,” said Bryan Barney, General Manager, Network Security Group, Sophos.

“Most notably, in the past year we’ve released our SG Series appliances, the fastest UTM devices we’ve ever produced and expanded the UTM protection we offer with our new cloud-based sandboxing, integrated mobile device management and really simple to use email encryption. Smaller businesses need effective security that is easy to use and that’s exactly what we provide. And it’s why we’re seeing more and more partners and customers switching to Sophos for their UTM and Next-Gen Firewall needs.”

In the most recent quarter of trading, April to June 2014, Sophos recorded a 27 percent increase in UTM sales, and a 33 percent increase in new customer business for UTM. This demonstrates the significant share gains the company is making; Sophos’ network security business now accounts for billings in excess of $150 million — with tremendous growth across North America, Asia Pacific and EMEA, among other regions. Additionally, the company’s “channel first” focus continues to deliver success with the signing of several new strategic channels to market such as the recently agreed distribution deal with Ingram Micro in North America. Sophos now has over 25,000 UTM channel partners worldwide, with the number of partners growing at over 20 percent a year.

According to Gartner, “the Leaders quadrant contains vendors at the forefront of making and selling UTM products that are built for midsize-business requirements. The requirements necessary for leadership include a wide range of models to cover midsize-business use cases, support for multiple features, and a management and reporting capability that’s designed for ease of use.

Vendors in this quadrant lead the market in offering new safeguarding features, and in enabling customers to deploy them inexpensively without significantly affecting the end-user experience or increasing staffing burdens. These vendors also have a good track record of avoiding vulnerabilities in their security products. Common characteristics include reliability, consistent throughput, and products that are intuitive to manage and administer.”

To download a complimentary copy of this report, click here.

You can read the original article, here.

15

Jan

Unfortunately, these companies don’t provide complete end-to-end encryption, and there are many loopholes the NSA, or cybercriminals, can slip through.

That’s why an encryption solution that protects data everywhere — in emails, on disk, or in the cloud — is essential. In this short video, we explain how you can get security and performance; plus how you can manage native encryption on Macs and Windows PCs, while also protecting data everywhere it resides.

James Lyne, global head of security research at Sophos, explains that many companies aren’t using encryption for fear of slowing users down. With Sophos, you don’t have to worry about encryption impacting performance, James says.

The new SafeGuard Enterprise solves the major challenge of managing encryption across multiple platforms, devices, and cloud environments. Users and IT staff can easily share data safely between Windows, Mac and mobile devices – securing data wherever it lives and wherever it is sent.

For more information about how to manage native encryption on Windows PCs with SafeGuard Enterprise, you can download our free whitepaper – Managing BitLocker With SafeGuard Enterprise (registration required).

What’s New in SafeGuard Enterprise 6.1

  • With SafeGuard Enterprise you can manage Microsoft BitLocker for Windows or Apple FileVault 2 for Mac from a single console.
  • Now with support for Windows 8, and file and disk encryption on Macs, SafeGuard covers more operating systems and platforms.
  • Simplified keyring creation grants you seamless, centralized management. With this newest release, you can save time with our key ring creation that requires no repeat login.
  • Centrally manage full-disk encryption and file encryption, wherever data is stored: removable media, network file shares and even in the cloud.
  • Get up-to-date security status for all your devices with reporting and auditing that lets you monitor and enforce compliance with internal policies and external regulations.

You can read the original article here.
15

Jan

Of 2,000 respondents surveyed globally, 58 percent confirmed that management does not see cyber attacks as a significant risk to their business. Despite this, IT infrastructure and asset security incidences, as well as wider security related disruptions, were found to have cost these SMBs a combined average of $1,608,111 over the past 12 months.

The research, sponsored by Sophos, also identified that the more senior the position of the decision maker in the business, the more uncertainty there was surrounding the seriousness of the potential threat.

“The scale of cyber attack threats is growing every single day,“ said Gerhard Eschelbeck, Chief Technology Officer for Sophos, “yet this research shows that many SMBs are failing to appreciate the dangers and potential losses they face from not adopting a suitably robust IT security posture.”

According to the research, there are three main challenges preventing the adoption of a strong security posture: failure to prioritize security (44 percent); insufficient budget (42 percent); and a lack of in-house expertise (33 percent). In many SMBs there is also no clear owner responsible for cyber security, which often means it falls into the purview of the CIO.

“Today in SMBs, the CIO is often the “only information officer”, managing multiple and increasingly complex responsibilities within the business,” said Eschelbeck. “However, these “OIOs” can’t do everything on their own and as employees are demanding access to critical apps, systems and documents from a diverse range of mobile devices, it would appear security is often taking a back seat.”

The study also reveals uncertainty around whether ‘Bring Your Own Device’ policies (BYOD) and the use of the cloud are likely to contribute to the possibility of cyber attacks. Seventy-seven percent of respondents said the use of cloud applications and IT infrastructure services will increase or stay the same over the next year, yet a quarter of those surveyed indicated they did not know if this was likely to impact security.

Similarly, 69 percent said that mobile access to business critical applications would increase in the next year, despite the fact that half believe this will diminish security postures.
 
“Small and midsize organizations simply cannot afford to disregard security,” said Larry Ponemon, president of the Ponemon Institute. “Without it there’s more chance that new technology will face cyber attacks, which is likely to cost the business substantial amounts. CIOs are under pressure to implement new technology that informs agile and efficient ways of working, but this should not take precedence over security. The industry needs to recognize the potential dangers of not taking cyber security seriously and create support systems to improve SMB security postures.”

The study targeted SMBs in the United States, United Kingdom, Germany and Asia-Pacific (Australia, India, China and Singapore) to better understand how such organizations are managing security risks and threats. Key findings of the study include:

  • Fifty-eight percent of respondents say management does not see cyber attacks as a significant risk.
  • One-third of respondents admit they are not certain if a cyber attack has occurred in the past 12 months. Forty-two percent of respondents said their organization had experienced a cyber attack in the past 12 months
  • Respondents in more senior positions have the most uncertainty about the threats to their organizations, indicating that the more removed the individual is from dealing on a daily basis with security threats, the less informed they are about the seriousness of the situation and the need to make it a priority.
  • CISOs and senior management are rarely involved in decisions regarding IT security priorities. While 32 percent say the CIO is responsible for setting priorities, 31 percent say no one function is responsible.
  • Forty-four percent of respondents report IT security is not a priority.  As evidence, 42 percent say their budget is not adequate for achieving an effective security posture.  Compounding the problem, only 26 percent of respondents say their IT staff has sufficient expertise.
  • Respondents estimate that the cost of disruption to normal operations is much higher than the cost of damages or theft of IT assets and infrastructure.
  • Mobile devices and BYOD are much more of a security concern than the use of cloud applications and IT infrastructure services. However, these concerns are not preventing extensive use and adoption of mobile devices, especially personal devices.

Uncertainty about their organization’s security strategy and the threats they face varies by industry:

  • Respondents in financial services have more confidence, which can probably be attributed to the numerous data protection regulations.
  • The technology sector is also more security aware, which is probably due to the IT expertise that exists in these organizations.
  • Retailing; education and research; and entertainment and media have the highest level of uncertainty about their organization’s security strategy and the threats they face.

Recommendations:

  • Organizations need to concentrate resources on monitoring their security situation in order to make intelligent decisions. While assessing where they stand on the security continuum, organizations need to focus on monitoring, reporting and proactively detecting threats.
  • Establish mobile and BYOD security best practices.  Carefully plan and implement a mobile strategy so that it doesn’t have an impact on the overall security posture.
  • Organizations should look for ways to bridge the gap created by a shortage of information security professionals.  Consider ways to free-up time for in-house resources, including a move to cloud technologies, security consulting and easy-to-manage solutions.
  • Measure the cost of cyber attacks, including lost productivity caused by downtime.  Work with senior management to make cyber security a priority and invest in solutions that restore normal business activity more quickly for a high return on investment.
  • Organizations in all sectors are regularly breached and regulations are often simply the beginning of properly securing a network.  Consider consolidated security management to gain a more accurate picture of threats that will help focus on problem areas.

A full copy of the Ponemon Institute study: The Risk of an Uncertain Security Strategy, is available here.

15

Jan

One of Negobot’s creators, Dr. Carlos Laorden, told the BBC that past chat bots have tended to be too predictable: “Their behaviour and interest in a conversation are flat, which is a problem when attempting to detect untrustworthy targets like paedophiles.” The most innovative aspect of Negobot may be a key differentiator that makes it appear more lifelike: namely, the incorporation of the advanced decision-making strategies used in game theory. In a paper about their creation, the researchers describe how they’ve taught the robot to consider a conversation itself as a game.

For example, the bot identifies the best strategies to achieve its goal in what its programmers have taught it to understand as a competitive game. Negobot’s goal is to collect the information that can help to determine if a subject involved in a conversation has paedophile tendencies, all the while maintaining a convincing, kid-like prattle, sprinkled with slang and misspellings, so the subject doesn’t get suspicious. Negobot keeps track of its conversations with all users, both for future references and to keep a record that could be sent to the authorities if, in fact, the subject is determined to be a paedophile.

The conversation starts out neutral. The bot gives off only brief, trivial information, including name, age, gender and hometown. If the subject wants to keep talking, the bot may talk about favorite films, music, drugs, or family issues, but it doesn’t get explicit until sex comes into the conversation. The bot provides more personal information at higher levels, and it doesn’t shy away from sexual content. The Negobot will try to string along conversationalists who want to leave, with tactics such as asking for help with family, bullying or other typical adolescent problems. If the subject is sick of the conversation and uses less polite language to try to leave, the bot acts like a victim – a youngster nobody pays attention to and who just wants affection from somebody. Robot. Image courtesy of Shutterstock.From there, if the subject has stopped talking to the bot, the bot tries to exchange sex for affection. Is this starting to sound uncomfortably like entrapment?

That’s exactly what gets some experts worried. John Carr, a UK government adviser on child protection, told the BBC that overburdened police could be aided by the technology, but the software could well cross the line and entice people to do things they otherwise might not: “Undercover operations are extremely resource-intensive and delicate things to do. It’s absolutely vital that you don’t cross a line into entrapment which will foil any potential prosecution.” The BBC reports that Negobot has been field-tested on Google chat and could be translated into other languages. Its researchers admit that Negobot has limitations – it doesn’t, for example, understand irony.

Still, it sounds like a promising start to address the alarming rate of child sexual abuse on the internet. Hopefully, the researchers will keep it reined in so as to avoid entrapment – a morally questionable road that could, as Carr pointed out, ruin the chances for prosecutorial success. What do you think? Are you comfortable with the premise, or does the chances of entrapment sour the concept for you?

You can read the original article, here.

15

Jan

Στο διάγραμμα που δημοσιοποιήθηκε από ανεξάρτητη εταιρεία ερευνών, και περιλαμβάνει τους Δείκτες Υπόσχεσης και Εκπλήρωσης, μπορείτε να δείτε και να συγκρίνετε την αποτελεσματικότητα ορισμένων από τις σπουδαιότερες εταιρείες της βιομηχανίας των υπολογιστών στο marketing αλλά και στην εκτέλεση.

Ένας κατασκευαστής, που βρίσκεται στο πάνω δεξί τεταρτημόριο του διαγράμματος, έχει βαθμολογηθεί με υψηλή βαθμολογία τόσο στο τομέα της υπόσχεσης όσο και στο τομέα της εκπλήρωσης αυτής της υπόσχεσης. Με βάση τα ίδια κριτήρια, μία εταιρεία στο κάτω αριστερό τεταρτημόριο, δεν τα καταφέρνει ούτε στο επίπεδο της υπόσχεσης, ούτε στο επίπεδο εκτέλεσης.

O “Δείκτης Εταιρικής Υπόσχεσης” (Vendor Promise Index) σχεδιάστηκε κατά τέτοιο τρόπο ώστε να μετράει την αποτελεσματικότητα του marketing. Χρησιμοποιεί τέσσερα από τα δεκατέσσερα σημεία αξιολόγησης πελατών (Θέση ανταγωνιστικότητας, Τεχνολογική Καινοτομία, το Στρατηγικό Όραμα του management της εταιρείας καθώς και η Μάρκα/ Φήμη) που σχετίζονται με ιδέες και concepts που μεταφέρονται σε πιθανούς πελάτες σε παγκόσμιο επίπεδο πριν το πραγματικό προϊόν ή κάποια υπηρεσία παραδοθεί προς χρήση.

Ο “Δείκτης Εταιρικής Ικανοποίησης” (Vendor Fulfillment Index) σχεδιάστηκε ως μέτρο για την εκτελεστική αποτελεσματικότητα. Χρησιμοποιούνται και σε αυτή τη περίπτωση τέσσερα από τα δεκατέσσερα κριτήρια  βαθμολόγησης πελατών  (Απόδοση/ Τιμή, Ποιότητα προϊόντος, Παράδοση σύμφωνα με την Υπόσχεση και Ποιότητα τεχνικής υποστήριξης) τα οποία σχετίζονται με το φυσικό προϊόν και την υπηρεσία που έχει παραδοθεί και την εμπειρία που είχε ο πελάτης από τη χρήση του συγκεκριμένου προϊόντος ή της υπηρεσίας.

Το μέγεθος του κύκλου που βλέπετε στο διάγραμμα επίσης δείχνει τη σχετικότητα μεταξύ των βαθμολογιών που έλαβε κάποια εταιρεία. Οι γραμμές που τέμνονται δείχνουν το μέσο όρο βαθμολογίας που έλαβε κάθε εταιρεία, συμπεριλαμβανομένων και εταιρειών που δεν βρίσκονται στο διάγραμμα. Όπως μπορείτε να δείτε, η Sophos έχει αποσπάσει εξαιρετική βαθμολογία, τόσο στο τομέα του marketing, όσο και στο τομέα του να κάνει πραγματικότητα όλα όσα υπόσχεται για τους πελάτες της.

15

Jan

We want to share a little tip – did you know that we offer an amazing alternative to cheap consumer grade Internet routers?

The difference is, our software is enterprise class, fully maintained and free. Here’s how you can try our Sophos UTM Home Edition and our free Sophos UTM Essential Firewall for businesses.

If you think you need to be truly “unlucky” to be targeted – try putting an unshielded Windows computer or a web server on the Internet and watch it being probed within seconds. This is not a matter of misfortune; it’s a matter of seconds.

Being such a critical piece of equipment you might think firewalls all come as cast iron, industrial strength appliances. But, as has been apparent, this is not the case.

Many times the software is not maintained on these devices. Some are not made to update automatically, or are difficult to upgrade. Or the vendor has simply stopped maintaining the software.

Let us give you some examples security weaknesses we’ve seen recently.

  • Admin access: this is the holy grail. Anyone can go in a reconfigure your router.
  • UPnP – an autoconfiguring standard to allow devices on your network to open up ports in your firewall

The good news is that the Sophos UTM Essential Firewall (for businesses) and Sophos UTM Home Edition address all the issues I’ve mentioned above.

  • We continuously maintain and update the software for it. This means we can make continuous improvements and quickly address any issues.
  • We don’t support UPnP so it will never be an issue
  • You get remote access so you can access you home network wherever you are without having to open any ports on the firewall

Try our Sophos UTM Home Edition, and our free Sophos UTM Essential Firewall for businesses.

You can choose how you deploy it:

  • Use an existing standard PC with at least two network cards
  • Install it as a VM in your virtual environment
  • Buy a hardware appliance from us
  • Or you can geek out completely and even run it in the Amazon EC2 cloud … the possibilities are endless


You can read the original article, here.

15

Jan

According to Gartner, Leaders are at the forefront of making and selling mobile data protection products that are built for enterprise business environments. The requirements necessary for leadership include a long-term road map that follows and/or influence Gartner, Inc’s vision of the developing needs of buyers in the market. Vendors in this quadrant lead the market by making their competitors’ sales staffs nervous and force competitors’ technical staffs to follow their lead. Their MDP products are well-known to clients and are frequently found on RFP shortlists.

To be positioned as a leader for the past nine years is a testament to our product teams who continue to deliver innovative encryption and data protection products,” said John Shaw, Vice President for enduser security products at Sophos. “An aggressive roadmap, coupled with our plans to make it even simpler for small and medium sized businesses to protect their data by encrypting drives, files, cloud storage and mobile files invisibly, positions us for even more success in the months and years ahead.

Sophos delivers leading solutions to help organizations protect critical assets. Sophos SafeGuard Enterprise protects data on desktops, laptops, removable media, file shares and to the cloud with proven, standards-based encryption—fully managed from one central console. Sophos also recently announced Sophos Mobile Control 3.5, the latest version of its award-winning mobile device management (MDM) solution, which now also supports iOS 7. Available both on-premise and as-a-service, Sophos Mobile Control 3.5 makes it simple for small and mid-market organizations to secure, monitor and control mobile devices.

Sophos was also positioned as a “Leader” in Gartner, Inc’s “2013 Magic Quadrant for Unified Threat Management.

15

Jan

Sophos received top marks in the latest report from AV-Comparatives, a leading international testing lab. The report, titled “Impact of Anti-Virus Software on System Performance,” evaluated twenty one of the world’s leading security products on a PC running under Windows 7.

The testing lab prepared a total of 545 infection scenarios, and Sophos’ antivirus offering tied for the highest score among the products reviewed. It also received an “Advanced +” award, based on the lab’s assessment of the overall results.

We value the work of independent testing labs like AV-Comparatives, as they help vendors like Sophos to strengthen our offerings, while providing consumers and businesses great insight so that they can make better informed decisions,” said Mark Harris, vice president, engineering, Sophos. “This latest recognition validates the great work of our team, which is committed to developing complete security solutions to combat advanced threats.

In related testing news, Virus Bulletin, another leading independent lab awarded Sophos with a VBSpam award for its comparative anti-spam testing. This marks the 20th time that Sophos has received this honor for its Sophos Email Appliance. Additionally, Sophos recently received a VB100 award for Sophos Endpoint Security and Control as part of Virus Bulletin’s comparative review on Windows XP Professional SP3.

Click here to see the original article.

15

Jan

“The new Sophos SG Series appliances are the fastest UTM and Next-Gen Firewall devices we’ve ever produced,” said Guenter Junk, Senior Vice President and General Manager, Network Security Group, Sophos. “They run our latest operating system, version 9.2, and are optimized to get the most out of latest performance innovations from Intel to ensure our customers and partners get an unrivalled performance and protection combination.”

The new SG Series includes models to meet the requirements of small offices to large, distributed enterprises. These 1U appliances are available today in the mid-range 200, 300 and 400 models.  They all deliver over 10 Gbit/sec firewall throughput to easily handle the demands of multi-layered protection. The SG Series is the 6th generation of Sophos security gateways built on an Intel® architecture, to enable Sophos customers to quickly benefit from the frequent performance and protection enhancements. They utilize Intel® technologies including high-speed LAN interfaces, high volume Solid State Drives and AES-NI acceleration.

“By using Intel® Architecture, Sophos has been able to use the performance gains we’ve been able to deliver with the 4th Generation Intel Core processors which delivers improved software processing architecture,” said Bob Ghaffari, Director, Communications and Storage Infrastructure Division, Intel. “Sophos has been able to see dramatic performance improvements by unlocking Intel’s core processor capabilities to make fast, intelligent decisions.”

The SG Series run the latest Sophos UTM 9.2 operating system which features over 150 enhancements including new Advanced Threat Protection and SPX Email Encryption functionality. Designed to run on an Intel architecture, version 9.2 can also be deployed on Intel compatible servers as virtual appliances and in the cloud using Amazon Web Services.

large-450

Bruce Kneece, Chief Technology Officer at Convergent Information Security Solutions, said, “Our team was heavily involved in the UTM 9.2 beta program.  From the outset we liked what we saw – added performance and simplicity across the board.  Version 9.2 running on the SG Series hardware is a true winner.  It’s easy for us to recommend it to our customers.”

large-625

Additional information on all of the features in Sophos SG Series appliances and Sophos network security solutions is available at: www.sophos.com/accelerated.  

15

Jan

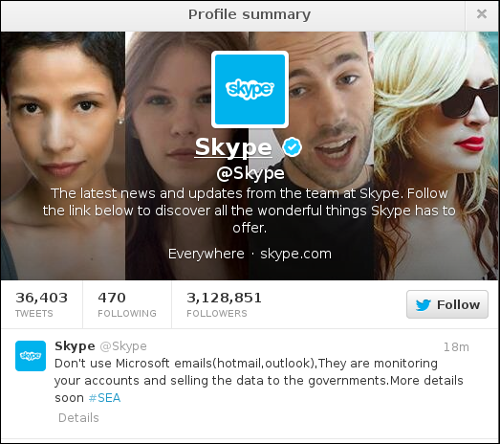
This isn’t entirely surprising as the FBI had issued a warning on Christmas Eve to media organizations about a new wave of phishing attacks associated with the infamous SEA. Skype has more than three million followers on Twitter, which indicates that, had the attackers wanted to send out malicious links or other dangerous content, this could have been a whole lot worse.

What I would like to know is why on earth a company social media profile with over three million followers would not be using two-factor authentication. Earlier this year Twitter rolled out an improved two-factor solution seemingly in response to previous attacks by the SEA. WordPress offers two-factor authentication and Facebook has supported two-factor authentication for a couple of years now, all in an attempt to prevent this exact type of attack.

Twitter 2 step

Microsoft, would you care to explain why you apparently are not using it? We believe it is the responsibility of organizations with a large number of followers to do whatever they can to secure their profiles. We suppose this can be a lesson to the rest of us. Take advantage of the safety net of two-factor authentication whenever possible. While it may be less than perfect, so are you.  

You can read the original article here.
15

Jan

Keenan brings more than 20 years of sales and sales management experience to Sophos, including 13 years with SonicWALL, where he most recently built a new sales organization for mid-market accounts and developed the division’s channel strategy. As vice president of North America Sales, Keenan grew the business by fostering key relationships with the company’s channel partners.

John Keenan is widely respected by the security channel, and I am thrilled to welcome him to Sophos. He brings a proven track record of success in the security space and has winning experience in leading channel and sales teams,” said Michael Valentine, senior vice president of sales for Sophos. “Every day, the Sophos team is working hard to be the preferred vendor in security for the channel and customers. Our products, our people and our partner programs continue to gain industry accolades. In bringing John aboard, we have an ideal leader for continued growth in our North American business.

I am excited to join Sophos; the company’s value proposition of ‘security made simple’ clearly resonates with customers and the channel,” said Keenan. “The company’s relentless focus on empowering the channel, a best-in-class portfolio of endpoint, mobile, server and network solutions, and the opportunity to contribute to Mike Valentine’s winning team made my decision to join Sophos an easy one.


15

Jan

McAfee may be big, but that doesn’t mean better. When you look at independent tests and evaluations, Sophos comes out on top. Get our Endpoint Buyers Guide to see all the research that will help you evaluate the top endpoint protection products.

This buyers guide shows you how we match up against McAfee and other vendors in performance, protection, ease of management and customer support.

Better performance

Your endpoint protection can’t come at the expense of user productivity.

In a recent AV-Comparatives performance test, Sophos Endpoint Protection had the best (lowest) system impact score, meaning our software had the least amount of impact on a computer’s speed in performing tasks like launching programs and files.

As you can see in the chart below, we have the industry’s lowest impact on performance, while McAfee scored at the bottom of the scale. In this comparison, a lower score means better performance.

Sophos gives you protection that won’t slow you down.

SophosVsMcAfee-AV-Comp-Chart

Better protection 

When you choose Sophos, you’re choosing better protection from malware.

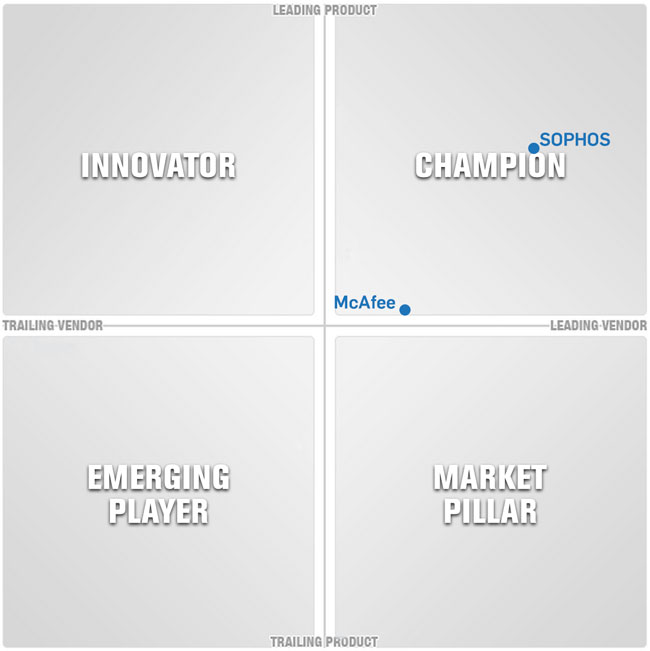
As you can see in Info-Tech’s latest Vendor Landscape: Endpoint Anti-Malware report, Info-Tech placed us far higher and to the right of McAfee, meaning we continue to beat McAfee with better protection against malware. This also proves how our strategy of complete security, our strong market presence, and our reputation as trendsetters in the industry leaves McAfee far behind.

Info-Tech Research Group has ranked us Champions for the last three years, recognizing our superior products based on features, affordability, usability, and architecture. In addition, Info-Tech evaluates vendors for viability, strategy, reach and channel.
SophosVsMcAfee-InfoTech-Chart

Fast on Macs

Here’s what a user from LowEndMac.com has to say about Sophos Endpoint Antivirus:

“With some antivirus suites for Windows you can really feel a difference in computer performance, sucking system resources and some even bring them down to a crawl. How does Sophos compare? I have been running Sophos on my 2009 MacBook running Mavericks for just over a week, and I haven’t noticed any performance drop since it has been installed.”

Read more about this review on our Sophos Blog.

Take a look at how we rank against other security vendors. Click the button below to download the Endpoint Buyers Guide.

Give Sophos a try

The best way to see how we perform is to give us a try. It’s easy to take a free trial of our Endpoint Antivirus. You can choose either on-premise or cloud deployment, and start your trial today.

You can read the original article, here.