PRODUCTS

Cyber Security Elements by NSS

News

19

Nov

AI agents can log in to business apps, query databases, call APIs and make changes to code. Each task may require credentials, creating a security risk when those credentials are shared, stored in plain text or allow access beyond what the agent needs to complete a task.

A safer approach is to give each agent a distinct identity and controlled access to credentials stored in an encrypted vault. Keep secrets out of prompts and code, limit access to the task at hand and log how credentials are used. These practices help teams manage agent access and respond when something goes wrong.

Why AI agents need credentials

An AI agent is software that can take actions to complete a goal. To work across business systems, it may need login credentials, API keys, database connection strings, SSH keys or certificates.

These credentials belong to Non-Human Identities (NHIs). Teams may create them quickly, overlook them during access reviews or give them broad permissions to avoid interrupting workflows. As organizations use more agents, they need a way to manage each agent’s credentials and track its access.

The risks of poor credential management

AI agents can encounter untrusted content and make decisions at runtime. That creates opportunities for credentials to be exposed or misused.

  • Prompt injection and credential misuse: Malicious instructions in a web page, email or document may try to steer an agent into exposing or misusing credentials.
  • Secrets in prompts and logs: Passwords or keys included in prompts, chat history or application logs may be accessible to people or systems that can view those records.
  • Hardcoded credentials: Secrets in source code, configuration files or .env files can be accidentally committed to a repository and may be difficult to rotate.
  • Excessive permissions: An agent with broad, long-lived access can cause more damage if it makes a mistake or is compromised.
  • Shared identities: When multiple agents use the same login, teams may not be able to determine which agent performed an action.

How to manage passwords and secrets for AI agents

AI agent credentials need to be protected throughout their lifecycle, from storage and access to rotation and review. These practices provide a practical way to manage that process.

Keep credentials out of prompts and code

Avoid putting passwords, API keys or other secrets in prompts, system instructions or source files. Instead, configure the agent to request access through an authenticated integration when a task requires it.

Store credentials in a secure vault

An encrypted vault gives teams a controlled place to store credentials and manage access. It can replace scattered files and shared documents with access controls and audit records.

Keeper Password Manager provides encrypted storage and access controls for credentials. For programmatic access to application secrets, teams may also need a secrets management solution.

Give each agent its own identity

Assign a distinct identity to each agent. Separate identities make it easier to trace activity, revoke access for one agent and limit the impact of a compromised credential.

Apply least privilege

Give agents only the access they need, scoped to the relevant system and action. A reporting agent that reads data should not have credentials that allow it to delete or change that data. When possible, limit access to the time needed to complete the task.

Use short-lived credentials where possible

Temporary credentials reduce the window in which a leaked secret can be used. Where systems require long-lived credentials, establish a rotation schedule and rotate them promptly if exposure is suspected.

Monitor access and require approval for sensitive actions

Log which agent accessed a credential and when. Review those records and alert on unusual requests, such as access to a system an agent has not used before.

For high-impact actions, such as production changes, financial transactions or privileged access, require human approval before the agent proceeds.

Password manager or secrets manager for AI Agents?

The right tool depends on the credentials and workflow.

A password manager is commonly used for login credentials, shared accounts and workflows involving both people and agents. A secrets manager is designed for programmatic access to API keys, tokens, certificates and other application secrets. Most organizations need both.

Using tools that support the relevant access controls and audit requirements can help teams manage credentials across human and machine workflows.

What a secure workflow looks like

An AI agent should retrieve credentials from an encrypted vault only when a task requires them. Access should be tied to the agent’s identity, limited to the permissions needed and recorded for review. Where supported, use credentials that expire after the task or rotate them regularly.

Developers using MCP or AI coding assistants can follow the same approach. Retrieve secrets at runtime through a secure integration and keep them out of configuration files and the model’s context.

Secure AI agent credentials with Keeper

Keeper helps organizations manage AI agent credentials with secure storage, controlled access and audit visibility. See how Keeper can help protect agent credentials across your environment.

Source: Keeper

17

Nov

After a very active Early Access Program with excellent participation by many of you, the product team is pleased to announce the release of Sophos Firewall v23.

What’s New:

Sophos Firewall v23 brings many of your top-requested enhancements in one feature-packed release. From new AI-powered assistance and a modern REST API to streamlined rule management, stronger high-availability protection, expanded identity support, and simpler day-to-day administration, Sophos Firewall v23 is designed to make your firewall easier to manage, automate, and scale, while further strengthening its Secure by Design foundation.

The new capabilities added in this release fall into five key areas:

1. AI and Automation

AI and automation tools are a few of the many highlights of Sophos Firewall v23. You can see these new solutions in action thanks to some helpful videos:

Sophos Firewall and AI Defense

Sophos AI Defense is a new Sophos Fusion solution that enables you to understand and control AI use across your environment, combining visibility, risk insight, and clear enforcement in one place. It utilizes Sophos Firewall as a key sensor and enforcement point. See how it works in this short video.

Sophos Firewall AI Assistant

Use the Firewall AI assistant in Sophos Fusion to work with your firewall rules using natural language chat. See it in action:

REST API

Sophos Firewall v23 implements a modern REST API with token-based authentication and OpenAPI 3.0 support that makes automation and integration easy. See how it works:

2. Simplified Management & Greater Resilience

Sophos Firewall v23 makes day-to-day administration easier and helps keep your network running smoothly, even under demanding conditions. Whether you’re managing a single firewall or hundreds, you’ll benefit from a redesigned rule management experience, improved visibility, faster performance, and significant enhancements to high availability.

What’s New:

  • Completely redesigned firewall rule management experience
  • Hardware-aware high availability monitoring and faster failover detection
  • Improved HA stability under heavy load
  • Automated firmware update scheduling in Sophos Central
  • Faster and more responsive administration interface
  • Improved navigation and firewall status visibility for administrators
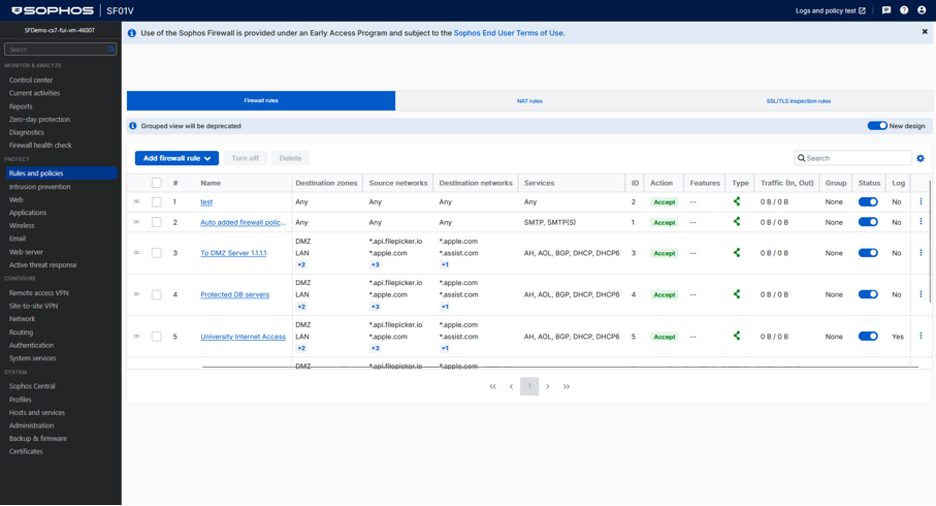
The new firewall rule management screen is just one of your many top-requested enhancements in Sophos Firewall v23

3. Secure by Design Enhancements

Sophos Firewall continues to build on its strong Secure by Design foundation with enhancements that further reduce your attack surface, improve security visibility, and simplify protection. New capabilities help secure DNS traffic, provide greater transparency into automated security updates, and make it easier to stay protected with the latest firmware and platform improvements.

What’s New:

  • DNS over HTTPS (DoH) support for stronger DNS security
  • Visibility into applied hotfixes and security updates
  • Modernized routing architecture and management
  • Improved threat response event handling
  • Additional platform hardening and security enhancements

Check out the new DNS enhancements:

4. Modern Identity & Access Integration

As many of you continue to adopt cloud and hybrid identity services, Sophos Firewall v23 expands integration options and simplifies authentication. You can more easily connect users across on-premises and cloud environments while improving MFA onboarding and extending support to a wider range of devices and deployment scenarios.

What’s New:

  • Entra ID support for Synchronized Security
  • Google Workspace identity provider integration
  • More secure MFA onboarding via email
  • Chromebook single sign-on support
  • Enhanced support for terminal servers and shared-user environments

See how to set up Google Workspace as an IdP:

5. Enhanced Scalability, Networking & Application Protection

Sophos Firewall v23 includes a wide range of infrastructure and networking enhancements designed to help support your growing environment. From major Web Application Firewall enhancements and a DHCP overhaul to expanded IPv6 support and improved service discovery, v23 delivers better scalability, performance, and flexibility.

What’s New:

  • Major Web Application Firewall performance and scalability improvements
  • Expanded WAF rule capacity and routing capabilities
  • New DHCP service architecture
  • mDNS reflector for education, campus, and segmented network environments
  • Enhanced IPv6 and IPoE connectivity support
  • Additional cloud platform deployment options

Summary

This release delivers 30 of your most-requested enhancements, helping you manage and secure your network more effectively. Every Sophos Firewall release continues to add tremendous value:

“Without a doubt, these changes are amazing and highly anticipated. In my opinion, they are even more impactful than many of the features introduced in version 22. It’s clear how much effort the team has invested in improving the platform. Congratulations to everyone involved.” 

– Sophos Firewall community member

A special thank you to everyone who participated in the Early Access Program!

More Details:

Review the What’s New Guide or Release Notes for full details.

Get Started Today

As with every firewall release, Sophos Firewall v23 is a free upgrade for Sophos Firewall customers with Enhanced or Enhanced Plus Support and should be applied to all supported firewall devices as soon as possible.

This firmware release will follow our standard staged roll-out process. The new v23 firmware will be gradually rolled out to all connected devices in phases over the coming weeks. A notification will appear on your local device or Sophos Fusion management console when the update is available, allowing you to schedule the update at your convenience.

If you want to get a head start, Sophos Firewall v23 can be downloaded directly from Sophos Fusion under the Licensing section of your account.

Source: Sophos
13

Nov

Your email provider manages your inbox. Who protects your email history?

Email outages happen. But losing access to critical business communications shouldn’t be part of the equation.

Recently, many organizations and businesses around the world realized how dependent their daily operations were on a single service. A widespread failure in the infrastructure behind a leading corporate email platform left companies on several continents unable to send, receive or even open their messages for hours. Sales teams lost contact with customers, finance departments could not retrieve approvals, and IT helpdesks were flooded with requests that could not be raised by email. In many cases, these numerous lost hours of productivity will add up to days of accumulated work.

Incidents like this are not new, and they will not be the last. Whether the cause is a faulty update, a configuration error, a cyberattack or a datacenter failure, the lesson is the same. Email is no longer just a means of communication. It is the working memory of an organization, holding contracts, quotations, invoices, technical decisions and legal evidence. When the mail server goes dark, that memory automatically goes dark with it.

Independent email archiving changes this picture. MailStore, a specialist in the field with more than 60,000 corporate customers in over 100 countries, keeps a one-to-one copy of every message in a central archive that is separate from the production mail server. Users can keep searching and reading their historical correspondence through the Outlook add-in, through MailStore Web Access in any browser, including on smartphones and tablets, or through the built in IMAP server. An archive does not replace the mail server for sending new messages, but it ensures that business knowledge is never held hostage by it.

MailStore’ s technology is designed for the long term. Journal archiving captures messages as they are sent and received, so even an email deleted from a mailbox has already been preserved. Existing mail from servers, email clients and PST files can be imported with each user’s folder structure intact, and a powerful full text search retrieves any message or attachment in seconds. Deduplication saves up to 70% of storage space, while SHA hashes and AES256 encryption protect archived data against tampering. Configurable retention policies support regulatory compliance, including the GDPR, and moving older mail out of the mail server keeps it lighter, faster and easier to back up.

For managed service providers, MailStore Service Provider Edition turns archiving into a branded, recurring revenue service that scales from a single server to a multi-server deployment.

MailStore’s solution is available through NSS, an international Value-Added Distributor specializing in cutting edge IT solutions for information security, networking, unified communications, data storage, virtualization and datacenter infrastructure. NSS supports its partners with pre-sales and after-sales services and training, helping them design an archiving strategy that suits each customer.

The next outage is a matter of when, not if. The question for every organization is whether its email history will still be within reach when it happens. Organizations that prepare today will treat the next incident as an inconvenience rather than a crisis. To learn more about MailStore’ s solution, contact the NSS team.

MailStore keeps your archived emails secure, searchable, and accessible independently of your primary email platform.
✓ Independent access to archived emails
✓ Fast search and retrieval
✓ Secure, long-term email archiving
✓ Compliance and retention support
✓ Greater control over your business data

Your email service may go down. Your business history doesn’t have to.
Don’t wait for the next outage.

Protect your email history with MailStore.

Contact NSS today to learn more.

10

Nov

AI doesn’t operate in isolation. Its prompts, workflows, data exchanges, and API calls all depend on the network. As organizations put AI to work, it adds a new layer of traffic that is increasingly encrypted, application-driven, and machine-to-machine.

Attackers are using AI too, helping them find weaknesses and act on them faster. The vulnerability you haven’t patched, the unsupported device you’ve forgotten about, or the management interface exposed to the internet can be discovered and exploited sooner. AI is narrowing the gap between exposure and attack. 

The network connects the users, devices, applications, cloud services, workloads, and AI systems that keep your organization running. That makes it one of the first places risk becomes visible and one of the fastest places to act. But only if the network has the performance to inspect demanding traffic, the visibility to recognize suspicious activity, and the ability to coordinate a response.

Four pressures reshaping today’s networks 

The challenges will be familiar to most IT and security teams. AI is increasing their scale, speed, and operational impact:

  • More demanding traffic. Encrypted, application-rich, and AI-enabled activity requires more inspection capacity. If the firewall becomes a bottleneck, organizations can be forced to choose between stronger protection and acceptable performance.
  • Faster-moving threats. AI can accelerate reconnaissance, vulnerability discovery, exploitation, and other stages of an attack, reducing the time defenders have to respond.
  • More blind spots. Distributed users, contractors, unmanaged and IoT devices, cloud services, and unsanctioned AI tools make it harder to see what is connected and govern how it is used.
  • Less time to respond. Disconnected tools, incomplete context, and manual handoffs make it harder to contain threats before they spread.

Performance and protection can no longer be planned separately 

This is not a reason to slow AI adoption. It is a reason to reconsider an old network trade-off. Organizations should not have to choose between supporting innovation and maintaining strong protection. Securing the AI-era network requires:

  • Protected performance: enough capacity to inspect encrypted and application-rich traffic with the necessary protections enabled, without slowing the business down.
  • Connected defense: network visibility and signals that strengthen investigation and response, helping security teams recognize and contain threats before they spread.

Three questions to ask about your network 

Securing the AI-era network is not simply a matter of buying a faster firewall. It means planning performance, visibility, and response together.

1.Can your network maintain performance with protection enabled?

Headline throughput tells only part of the story. Capacity planning should reflect the TLS inspection, threat prevention, application control, and other protections you expect to keep switched on.

2.Can you see beyond traditional network boundaries?

Users, contractors, SaaS applications, unmanaged devices, and AI services all contribute to your exposure. Your visibility needs to extend across the environments where work now happens.

3.Can network activity trigger a coordinated response?

A network anomaly becomes more valuable when your team can investigate it alongside endpoint, identity, application, and threat context, then take action before the threat spreads.

The goal is a network that can see what is connected, understand what is happening, maintain protection without compromising performance, and help stop threats before they spread. 

How Sophos is helping secure the AI-era network 

Sophos Fusion provides the foundation for our connected approach to cybersecurity, bringing Sophos products, services, and security intelligence together to help organizations see more, understand more, and respond faster. For the network, that means connecting protection, visibility, and context across the places where users, devices, applications, and data come together.

The latest Sophos network security innovations build on that foundation:

Together, they extend the Sophos Fusion story into the network, helping organizations maintain performance, reduce blind spots, and respond faster.

Sophos Firewall v23: More control with less operational effort 

Sophos Firewall v23 helps organizations improve visibility, simplify administration, and strengthen resilience. It includes more than 30 enhancements, many based directly on customer and partner feedback.

  • See and control AI use. Integration with Sophos AI Defense adds network-level visibility, reporting, and policy enforcement for AI services.
  • Simplify firewall administration. The AI Assistant turns plain-language requests into proposed firewall rules that remain disabled until an administrator reviews and enables them. Redesigned rule management and an updated REST API make day-to-day administration and automation easier.
  • Improve resilience. Faster high-availability failover, visible hotfix status, firmware update scheduling, and DNS over HTTPS help organizations maintain protection and availability.
  • Protect more users and applications. Support for Microsoft Entra ID and Google identity providers, together with increased Web Application Firewall scale, helps protect larger and more diverse environments.

Learn more about Sophos Firewall v23 

New XGS 1U firewall appliances: More performance. More choice. 

We’re also adding four new models to the XGS 1U range: the XGS 2380, XGS 3380, XGS 4580, and XGS 5580. They give mid-sized and distributed organizations more options on price and performance:

  • Keep inspection switched on as traffic grows. Major gains in threat protection and TLS inspection performance, up to four times higher than comparable existing models, give you room to decrypt and protect growing volumes of encrypted traffic.
  • Get more from every watt. Two purpose-built Xstream FastPath designs improve performance per watt, helping lower operating costs over the life of the appliance.
  • Support higher-speed connectivity. 2.5G interfaces come on every new model, with up to 25G fiber on the XGS 3380 and above.
  • Reduce downtime. Field-replaceable SSDs mean only a faulty drive needs to be returned, while the appliance stays in the rack. Improved internal redundant power options add further resilience.

The new models expand the XGS range rather than replacing the existing appliances. The right choice depends on the protected performance, connectivity, resilience, and growth headroom your organization needs. Your Sophos partner can help you choose and size the right model for your environment.

Xstream Plus: Expand protection with one firewall license 

Xstream Plus is a new Sophos Firewall term license for organizations that need more than network-edge protection alone. It includes everything in our most popular subscription bundle, Xstream Protection, together with:

  • a model-specific allocation of Sophos Workspace Protection licenses
  • Enhanced Plus Support
  • up to one year of Sophos Fusion Firewall Reporting data retention, depending on traffic volume

This gives organizations a simpler way to extend secure access and browser-based controls to remote and hybrid users, strengthen support for business-critical deployments, and retain reporting data longer for investigations, trend analysis, and compliance needs.

Sophos NDR: Find and stop threats beyond the firewall 

Not every threat crosses a firewall, and not every device can run an endpoint agent. Now available as a standalone solution, Sophos NDR analyzes network activity to identify suspicious behavior across managed, unmanaged, IoT, and other agentless devices. It combines AI- and machine learning-powered behavioral detection with deep packet inspection and IDS/IPS capabilities.

  • Reveal activity other controls may miss. Detect suspicious behavior and lateral movement across managed, unmanaged, and agentless devices.
  • Disrupt malicious activity in real time. In Active Inline mode, Sophos NDR can drop identified malicious packets before they reach their target.
  • Deploy it to suit your network. Choose virtual deployment, compatible third-party hardware, or a purpose-built Sophos NDR appliance, with Active Inline, Passive Inline, and SPAN/TAP options.
  • Investigate with broader context. Bring NDR detections and network context into Sophos Fusion alongside information from other Sophos defenses.

Sophos NDR works alongside Sophos Firewall to provide a more complete view of the network. Sophos Firewall controls traffic at key network boundaries, while Sophos NDR analyzes activity inside the network to identify threats that boundary controls may not see. Both contribute network context through Sophos Fusion.

Sophos Workspace Protection: Secure access wherever work happens 

Sophos Workspace Protection helps secure how users access web, SaaS, private applications, and AI tools from anywhere, including from unmanaged contractor and BYOD devices. A model-specific allocation of Sophos Workspace Protection licenses is included with Xstream Plus, giving organizations a straightforward way to extend secure access and browser-based controls beyond the office.

As we connect more Sophos solutions, customers will be able to apply protection more consistently across the network, endpoint, and workspace. New synchronized web policies are an important step in that direction. Administrators can configure web filtering in Sophos Fusion and apply it across Sophos Firewall and Sophos Endpoint.

A Generative AI web category adds control over which AI services users can access, helping organizations allow approved tools, block unsanctioned services, and reduce the risk of sensitive information being shared inappropriately. Additional policy support for Sophos Protected Browser and Sophos DNS Protection is planned for future releases.

We’re also extending this connected approach to AI security. Integration between Sophos Workspace Protection and Sophos AI Defense is planned to bring additional visibility and control to how organizations use AI services.

A more connected view of network risk 

Each solution contributes a different part of the picture. Sophos Firewall provides visibility and control at key boundaries. Sophos Wireless and Sophos Switch show what is connected and where. Sophos NDR identifies suspicious activity inside the network, including on devices that cannot run an agent. Sophos Workspace Protection extends secure access and browser-based controls to users wherever they work.

Sophos Fusion brings more of this context together, helping security teams investigate activity across the network and coordinate a faster, better-informed response. Instead of treating each network signal in isolation, teams can use it as part of a broader view of risk.

Prepare the network for what comes next 

AI is making the network more important, not less. It is increasing organizations’ dependence on encrypted, application-driven, and machine-to-machine communication, while giving attackers new ways to find and exploit weaknesses faster.

The answer is not to slow innovation. It is to build a network that can maintain protection as traffic evolves, reveal activity across managed and unmanaged environments, and turn network signals into faster action. By planning performance, visibility, and response together, organizations can adopt AI with greater confidence without allowing security or user experience to become the constraint.

To explore the latest Sophos Firewall, XGS appliance, Sophos NDR, and Sophos Workspace Protection innovations, contact your Sophos partner or visit the relevant product web pages.

Source: Sophos

6

Nov

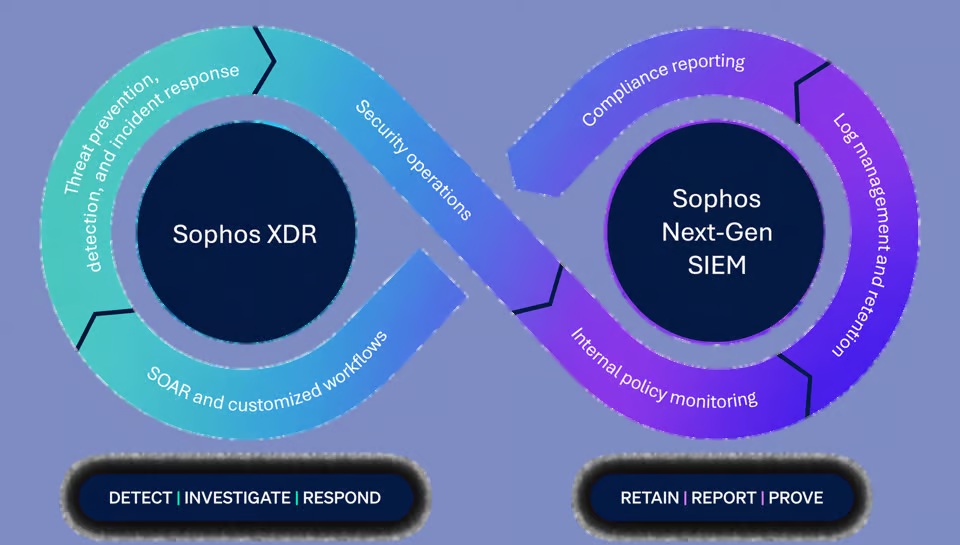
A SIEM is a multipurpose tool. It brings together cyber and physical security use cases; drives threat detection, investigation, and response (TDIR); serves as a system of record for governance, regulatory, and compliance needs; and supports observability use cases tied to resilience and service degradation. The list goes on.

In short, a SIEM is what an organization wants it to be. Therein lies both its strengths and its weaknesses.

The SIEM paradox

A SIEM can be a powerful “single pane of glass.” But that strength comes with two persistent challenges: operational complexity and data-ingestion costs.

Does more data mean better outcomes?

SIEMs store vast amounts of data. As the attack surface expands, organizations keep adding sources. Yet not all data serve the same purpose:

  • Detection and prevention require one set of data.
  • Investigations need contextual data to explain what happened.
  • Audit and compliance depend on evidence retained for reporting and review.

Because teams cannot always predict what they will need in the future, the default is often to ingest everything “just in case.” That is where the problems begin to compound.

Complexity comes first

The first symptoms are operational. Teams must determine which data is useful, why it matters, and how it should be applied in a particular context. Then they must be able to find it, search it, report on it, and turn it into something actionable when the moment comes.

Then comes the bill

Once the operational burden is established, the financial impact follows, often in the form of escalating ingestion costs.

How the SIEM became the center of the SOC

Over time, the SIEM also subsumed technologies that had once stood alone such as threat intelligence platforms, user and entity behavior analytics (UEBA), and security orchestration, automation, and response (SOAR). Each addition promised better context, stronger detection, or a tighter response loop.

Very quickly, the SOC was built around the SIEM, and the SIEM became fossilized in SOC processes and vendors took advantage of the “lock in”. Enter the era of SIEM deconstruction, and with it, the promised benefits of going “SIEM-less.”

Deconstructing the SIEM

Ingestion-based pricing crushing you with costs? Not to worry. Add a smart ingestion pipeline that filters out what you do not need before you store it. While you are at it, run detections in the pipeline. Et voilà, you have reduced storage costs and gained detections along the way.

Need to search the data in place? Add another component that can search across sources by translating queries for each one. Need to triage and investigate all those “detections” to determine what is worth chasing? Add an agentic SOC that promises to automate it all away.

Pretty soon, the collection starts to sound a lot like security information and event management, a SIEM. The difference is that the costs are now spread across individual components. It starts to look like unbundled pricing, where savings in one place create compute costs, or compromises, somewhere else.

The real cost driver: Compute

It is important not to confuse data-ingestion costs with storage costs. Processing data for upstream use cases requires compute; deciding how much data to retain, and for how long, requires storage. Even at today’s storage prices, compute costs dwarf storage costs.

Compute is the real cost driver. It is consumed when data is filtered, indexed for faster retrieval, queried, or used to generate reports. More compute is required when data must be rehydrated, moved from cold storage back into hot storage for analysis. Any or all of these costs can ultimately be passed on to the buyer.

A deconstructed architecture does not eliminate the underlying tasks or the ‘jobs to be done’. They still exist; they are simply carried out differently than they would be in a traditional SIEM.

Is SIEM-less a bad idea?

Actually, no. It can be the right call for an organization with the expertise and resources to build and maintain such a system. These new approaches are reshaping the economics and forcing traditional vendors to rethink their go-to-market strategies.

But a SIEM is ultimately a set of capabilities assembled into an architecture. Over time, every vendor offering one piece of the SIEM-less story will add adjacent capabilities until the resulting offering starts to look like, you guessed it, a SIEM.

Organizations that need a SIEM, therefore, face a practical choice: take the DIY route or invest in a fully integrated system with the right economics. At the end of the day, that choice matters.

Source: Sophos

3

Nov

Keeper Security, the leading zero-trust and zero-knowledge identity security platform, today announces Phishing Protection, a new feature in the Keeper Browser Extension that warns users before they enter credentials on fraudulent login pages. Built on a zero-knowledge local AI engine, the feature detects look-alike domains, spoofed websites and brand impersonation directly in the browser, helping users avoid handing over credentials to a cybercriminal.

Credential abuse was involved in nearly 40% of breaches, according to the 2026 Verizon Data Breach Investigations Report. Attackers now use generative AI to craft look-alike domains and deceptive login portals to harvest users’ credentials. However, these malicious websites often bypass traditional security filters. Keeper’s Phishing Protection addresses that gap. The feature runs on the user’s device and uses local machine learning to examine websites. The local AI model uses a zero-knowledge security architecture, meaning the user’s data is never shared.

“Phishing attacks are no longer simple email scams; they are highly automated, AI-driven operations designed to trick users into handing over sensitive credentials and information,” said Darren Guccione, CEO and Co-founder of Keeper Security. “When an adversary sets up a look-alike domain, form field or unofficial login portal, traditional security controls often fail to identify the threat until the damage is done. By embedding zero-knowledge AI into our browser extension, Keeper stops credential harvesting at the point of entry, giving individuals and organizations greater security and control.”

How phishing protection works

The local AI engine automatically evaluates web pages for structural indicators commonly associated with credential-harvesting sites, including:

  • Domain Impersonation: Look-alike characters (typosquatting) and brand names hosted on unofficial domains.
  • Obfuscated Infrastructure: Login details hidden within URLs, suspicious IP addresses and unusual link structures.
  • Deceptive Requests: Unofficial or untrusted sites actively requesting password inputs.

When Keeper detects a suspicious site, it immediately notifies the user and details the specific threat pattern identified. Users can view the threat breakdown, disable Keeper on that site or dismiss the warning. Enterprise administrators and individual users can restore access or re-enable autofill at any time from their blocked-sites list.

User authority and administrative control

Designed for privacy-first credential defense, the feature is entirely optional and disabled by default. IT administrators can enable and manage Phishing Protection centrally through the Keeper Admin Console, and end users can configure their own settings in the browser extension.

“Security controls have to work at machine speed, and they cannot come at the expense of the zero-knowledge guarantees our customers depend on,” said Craig Lurey, CTO and Co-founder of Keeper Security. “We engineered this AI engine to execute entirely on the local device using the customer’s private key. It delivers continuous, proactive verification of web assets, ensuring that autofill is protected against sophisticated domain spoofing without creating a privacy trade-off.”

Phishing Protection is available now as an opt-in feature in the Keeper Browser Extension, version 18.2.0. To learn more about Keeper’s zero-knowledge security architecture, visit keepersecurity.com.

Source: Keeper Security

30

Oct

Identity has become one of the most targeted attack surfaces in cybersecurity, with attackers increasingly relying on stolen credentials, compromised sessions, excessive privileges, and identity misconfigurations to gain access. At the same time, organizations are managing more cloud services, remote users, non-human identities, and a rapidly growing number of AI agents that can access systems and data.

According to the Sophos State of Identity Security Report 2026, 71% of organizations experienced an identity-related breach in the past year, with weak non-human identity management linked to 41% of these breaches.

The challenge is clear: it’s not just about managing identities, it’s understanding which identities introduce risk, how those risks evolve over time, and how to respond before attackers can take advantage.

Identity security is evolving. So is Sophos ITDR.

Sophos Identity Threat Detection and Response (ITDR) was introduced in 2025 as a powerful identity security add-on for Sophos XDR and Sophos MDR. Today, as organizations navigate this expanding identity attack surface, Sophos ITDR has evolved into a standalone solution and one of the fastest ways to experience Sophos Fusion, the Sophos AI-Native Cybersecurity Defense System.

What’s new in Sophos ITDR:

Now available standalone | Fast deployment, immediate visibility, no additional Sophos solutions required Expanded Microsoft support | Secures Microsoft Entra ID and on-premises Active Directory environments Dynamic AI identity risk scores | Continuously evaluate and explain risky identities using behavioral and environmental signals
AI identity visibility | Discovers Microsoft AI agents, ownership relationships, permissions, and risks 160+ continuous posture checks | Surface security gaps, excessive privileges, and identity attack paths Contextualized cases and direct response | Automatically group findings into cases and take key actions from one interface

Together, these enhancements help organizations move beyond identity management. Sophos ITDR supports full identity security, from visibility and prioritization to investigation and response.

Secure identity from risk to response

With a complete view of human and non-human identities and more than 160 continuous posture assessments, organizations can clearly see their users, devices, applications, groups, service accounts, and Microsoft AI agent access, owners, and permissions, at a glance.
Sophos ITDR then prioritizes what matters most through new dynamic, AI-driven identity risk scores that continuously evaluate and explain the risk of every human and non-human identity using behavioral analytics, authentication history, geolocation data, and other signals. Security teams can quickly understand who presents the greatest risk and why.

When credentials are exposed, Sophos ITDR continuously monitors dark web and breach intelligence sources and finds affected identities (with advanced monitoring of VIP accounts) and enables immediate action. High-risk findings are automatically grouped into contextualized cases that bring together identities, detections, and other risk factors all in one place. From there, organizations can respond directly from within Sophos ITDR by forcing password resets, revoking active sessions, enforcing MFA, and disabling accounts before attackers can turn exposed identities into active compromises.

Real results in minutes

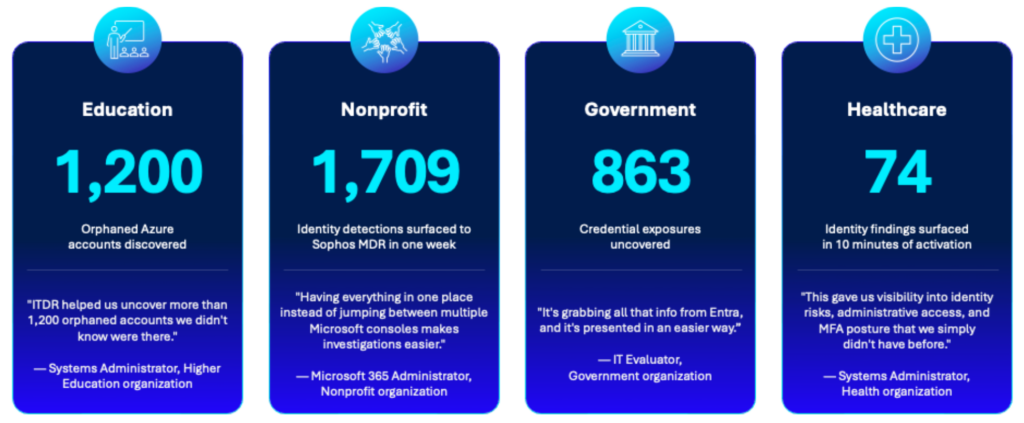
With a 30-day free trial and seamless deployment, organizations typically begin uncovering meaningful identity risks within minutes. In recent Sophos ITDR trials, organizations identified hundreds of orphaned Azure accounts, credential exposures, and critical MFA gaps that had previously gone unnoticed.

Immediate real-world customer findings from Sophos ITDR free trials:
Part of Sophos Fusion

Sophos ITDR is the identity layer of Sophos Fusion, the Sophos AI-Native Cybersecurity Defense System. As part of Sophos Fusion, identity intelligence becomes part of a broader cyber defense strategy that connects detection, investigation, and response across endpoints, networks, cloud environments, email, and identity systems. Learn more at www.sophos.com/fusion.

Get started today

Sophos ITDR supports both Microsoft Entra ID and on-premises Active Directory environments. To learn more, visit www.Sophos.com/ITDR or start a free 30-day trial to discover identity risks in minutes.

Source: Sophos
26

Oct

Remote access has become one of the most important (and least understood) identity, privilege, and zero trust control points in operational technology. Learn why the market is shifting from secure connectivity to secure remote operations, and how BeyondTrust and Xalient help organizations govern access, protect credentials, and reduce shadow access without disrupting operations.

Why OT Remote Access Is Now a Zero Trust Priority

Remote access has become one of the most overlooked risks in operational technology (OT)— and one of the hardest to control.

The business needed remote access. OEMs needed to support equipment. Engineers needed to troubleshoot across distributed sites. Operators needed to maintain uptime. Security teams, however, were often left trying to manage a patchwork of VPNs, jump boxes, shared accounts, remote desktop tools, vendor tunnels, and undocumented access paths that were introduced because the operational need was real.

That compromise is now reaching its limit.

In practice, OT remote access is no longer just a connectivity issue. It’s become one of the most important identity, privilege, and zero trust control points in the modern enterprise. The Gartner® Market Guide for CPS Secure Remote Access makes this very clear.

The market is moving from secure connectivity to secure remote operations, because cyber-physical systems (CPS) require more than traditional IT remote access patterns. In their report, Gartner® projects that by 2029, more than 20% of attacks on cyber-physical systems will use remote access vectors. That is a major signal for boards, CISOs, infrastructure leaders, plant managers, and operations teams.

The issue isn’t that remote access exists. Remote access is now an operational requirement. The issue is that many organizations don’t know all the remote access paths that exist, cannot consistently govern them, and cannot always prove who accessed what, when, why, and what they did once connected.

That’s where the real risk sits.

The OT Remote Access Problem Has Outgrown the VPN Conversation

It’s easy to say, “replace the VPN.” That is directionally right, but it’s not a complete strategy.

The deeper problem is that many OT environments were never designed for today’s remote operating model. They were built around availability, safety, uptime, segmentation, and specialized engineering workflows. Then digital transformation, IT/OT convergence, OEM support models, cloud connectivity, IoT, and workforce shortages changed the reality.

Now, organizations need remote access that is secure enough to effectively manage cyber risk, but practical enough for operations.

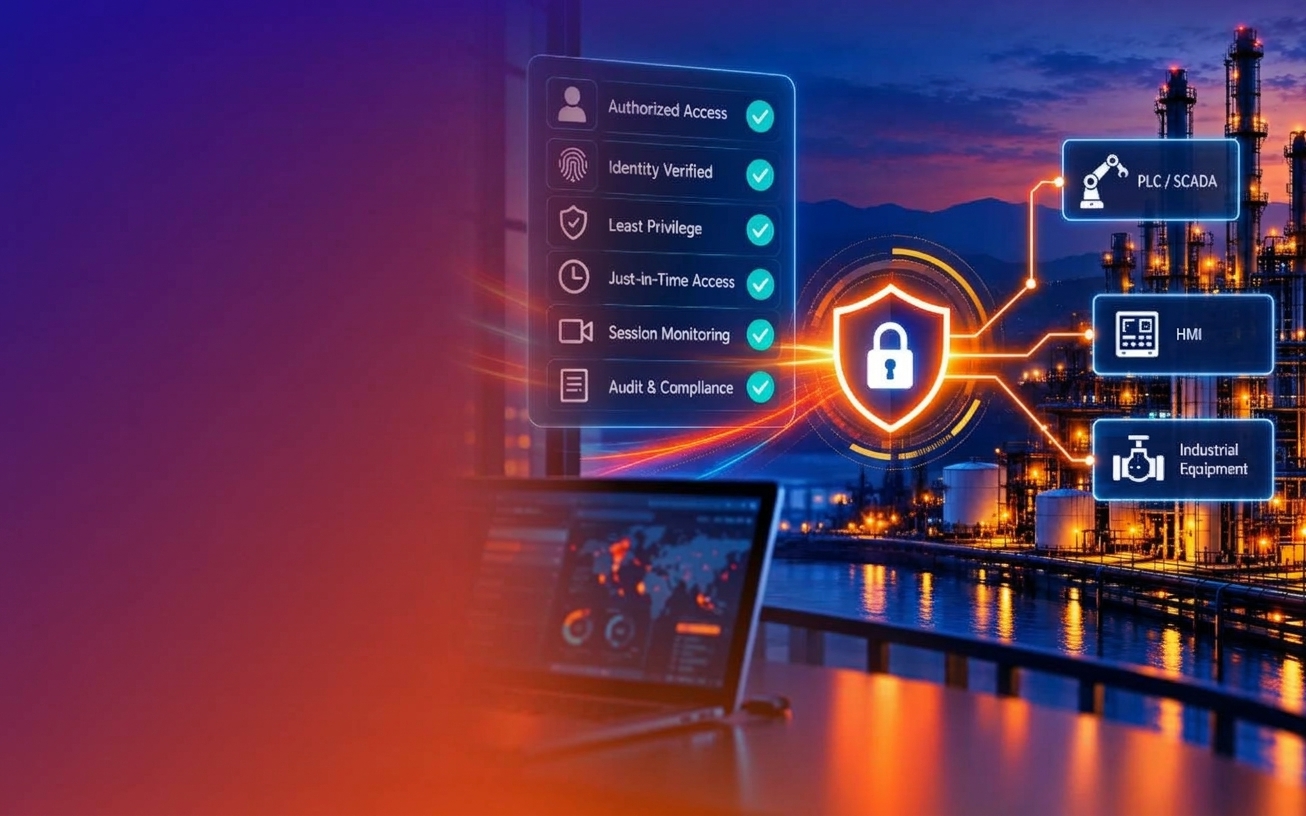
That means the new standard cannot be broad network access. It has to be:

  • Identity-secured access
  • Least-privilege access
  • Just-in-time (JIT) access
  • Session-monitored access
  • Credential-protected access
  • Operationally aware access
  • Auditable access

This is why BeyondTrust’s OT positioning is highly relevant. Its OT security message focuses on helping organizations secure industrial networks without disrupting productivity, safety, or compliance. It calls out the same themes we see in the field every day: IT / OT convergence, poor password security, unsegmented networks, and visibility gaps across connected systems and remote access methods.

That matters because OT security cannot be positioned only as a cybersecurity initiative. It must be positioned as a resilience, safety, operational continuity, and risk reduction initiative.

Where BeyondTrust Fits

BeyondTrust brings a strong and practical control set into this conversation.

Their OT solution centers around Privileged Remote Access, Password Safe, and Endpoint Privilege Management. In OT terms, that means they can help organizations reduce dependency on traditional VPNs, secure vendor and operator access, enforce least privilege, apply just-in-time (JIT) controls, record sessions, manage privileged credentials, and support zero trust objectives across industrial environments.

On their OT assessment page, BeyondTrust frames the problem well: modern OT systems depend on off-site vendors, operators, and employees, which creates new security risks as historically closed environments are opened for remote access. The free assessment is positioned around identifying the appropriate remote access and compliance solution for ICS and OT environments, with an emphasis on business continuity, safety, compliance, secure infrastructure access, and critical system protection.

This is the right conversation to be having.

The value is not simply that BeyondTrust can broker remote access. The value is that it can help bring remote access into a governed privileged access model. That includes visibility and control over remote sessions, least privilege enforcement, network segregation, simplified workflows, and comprehensive audit trails.

For many organizations, that’s a meaningful step forward from VPNs, shared credentials, unmanaged vendor tools, and loosely governed jump server access.

Where Xalient Fits

This is where Xalient and BeyondTrust create the most value together. BeyondTrust provides a strong technology foundation for privileged remote access, credential security, least privilege, and session governance. Xalient brings the advisory, architecture, integration, and execution experience needed to make those controls work in the real world.

That distinction matters.

Most clients do not simply need another tool. They need a clear operating model. They need to know what remote access exists today. They need to understand which OEMs, contractors, vendors, employees, and service providers have access. They need to identify where shared credentials are being used. They need to uncover shadow access. They need to define who approves access, how long it should last, what systems can be reached, what actions are allowed, and how the session is monitored.

They also need to do all of this without breaking operations.

That is where Xalient can lead with an advisory-first approach, then bring BeyondTrust into the right places in the architecture.

Together: BeyondTrust helps secure the access. Xalient helps design, integrate, operationalize, and govern the model.

The combined value can be positioned around five outcomes:

1. Discover and reduce shadow access

Gartner® is right to call out shadow access as an immediate concern. Many organizations have undocumented vendor connections, legacy VPNs, remote support tools, OEM tunnels, cellular access, shared accounts, and local workarounds that bypass formal governance.

Xalient can help clients assess and rationalize those remote access paths. BeyondTrust can then help bring privileged access into a more centralized, auditable, and controlled model.

2. Replace broad network access with controlled operational access

The old model gave users access to a network segment. The new model should give users access to the specific asset, application, or session required for the task.

BeyondTrust’s Privileged Remote Access aligns well here, especially around least privilege, JIT access, application access independent of network access, per-session MFA, activity recording, and reducing reliance on VPN-based access patterns.

Xalient can help design the target architecture, align it to the Purdue Model, and integrate the access pattern with identity providers, ITSM workflows, PAM governance, secure networking, and OT visibility tools.

3. Govern third-party and OEM access

Third-party access is one of the most urgent OT use cases. OEMs need access to support equipment and service-level agreements, but that access cannot be open-ended, undocumented, shared, or over-permissive.

The right model should include named users, approved access windows, ticket-based workflows, credential injection, session monitoring, automatic revocation, and clear evidence for audit.

4. Protect credentials and remove standing privilege

OT environments often include shared accounts, embedded credentials, default passwords, hardcoded credentials, service accounts, local admin rights, and legacy authentication patterns.

BeyondTrust Password Safe is relevant here because it provides discovery, onboarding, vaulting, rotation, credential injection, support for SSH keys and secrets, non-human accounts, and break-glass access.

Xalient can help clients define the credential strategy, prioritize the highest-risk assets and accounts, build the onboarding roadmap, and connect credential governance back to broader identity security and compliance requirements.

5. Build secure operations, not just secure access

This is the most important shift.

In OT, the goal is not simply to authenticate a user and establish a secure tunnel. The goal is to protect operations. That means safety, uptime, integrity, change control, visibility, and accountability have to be part of the access model.

Gartner®’s language around secure remote operations is important because it reflects where the market is going. OT remote access must become more granular, identity-centric, protocol-aware, auditable, and aligned to operational risk.

Xalient can help clients mature from tool deployment to operating model transformation.

OT remote access is becoming a strategic control point for identity-centric zero trust, and BeyondTrust plus Xalient can help clients modernize that control point without disrupting operations.

Next Steps to Improving OT Security

The first step is gaining visibility. Organizations need to understand exactly how remote access is used across their OT environments—who has access, how it’s granted, and how it’s controlled.

From there, Xalient and BeyondTrust can help clients move from fragmented access to governed access, from standing privilege to JIT, from shared credentials to accountable identities, and from remote connectivity to secure operations.

The future of OT security isn’t just about keeping attackers out. It’s about making sure every connection into the operational environment is known, justified, controlled, monitored, and aligned to the safety and resilience of the business.

Source: BeyondTrust

21

Oct

Fortra’s WebMail Catcher model helps detect malicious or suspicious emails sent from legitimate personal email services, where traditional infrastructure-based checks may fall short. It analyzes language, sender identity, communication history, campaign activity, and message metadata to distinguish everyday webmail communication from scams like gift card fraud, achieving over 99% precision in production.

Why Trusted Webmail Domains Can Still Deliver Email Threats

An email arrives from a familiar webmail provider. The sending infrastructure is legitimate, and there are no suspicious attachments or malicious links. Yet the message asks an employee to purchase gift cards, change payroll details, or respond to a fraudulent financial request. These attacks expose a challenge for email security: reputable services can carry dangerous messages. Checking where an email originated provides valuable information but understanding whether the message itself deserves trust requires additional context.

Fortra developed the WebMail Catcher (WMC) model to address this challenge. WMC focuses on messages originating from personal email services, including webmail providers and Internet Service Providers (ISPs), to identify potentially malicious emails and spam that can escape defenses focused on sending infrastructure.

Personal email services support a wide range of legitimate communications. Employees send documents from their personal accounts, independent professionals contact customers, and individuals communicate with businesses. Blocking messages simply because they originate from these services would disrupt routine work.

Attackers can use the same infrastructure to deliver social engineering scams. When the attack depends on persuading a recipient to act, there may be no harmful file or website to detect. The warning signs instead emerge from the language, sender identity, communication history, and broader sending behavior.
The Model 

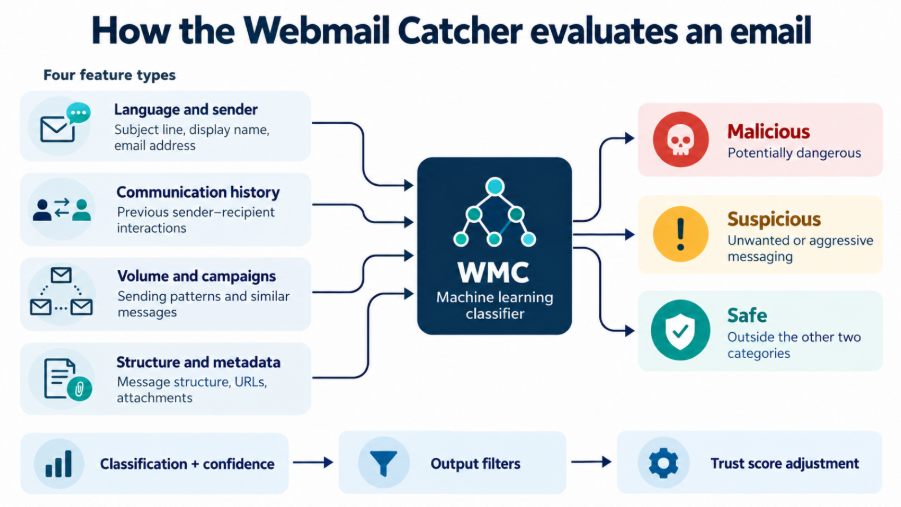
The WMC is a classical Machine Learning (ML) model that combines these signals together through feature engineering. It classifies each eligible message into one of three categories:

  • Malicious: Potentially dangerous emails.
  • Suspicious: Unwanted messages, such as aggressive marketing, that are not necessarily dangerous.
  • Safe: Messages that cannot be considered malicious or suspicious.

The features can be grouped into four main types:

  • Language and sender information: Natural Language Processing (NLP) models provide signals about subject-line topic, suspiciousness, and attention-seeking language, alongside classifications of display names.
  • Communication history: User Profiling Infrastructure (UPI) features capture previous inbound and outbound interactions, including counts and age-related measures. These help the model evaluate the relationship between sender and recipient.
  • Sending volume and campaign activity features describe sending volumes, the number of organizations receiving similar messages, and whether an email belongs to a detected campaign.
  • Message structure and metadata: Additional signals include message structure, URL counts, attachment presence, and text-based comparisons involving sender and recipient information.

These signals give the classifier context that any individual indicator would lack. An unfamiliar sender is not automatically malicious, and an attention-grabbing subject line can appear in legitimate correspondence. Their significance depends on the concurrent evidence found in the message.

Examples

Consider an illustrative gift card scam. A personal email account sends an employee a message with the subject:

“Need a quick favor”  

followed by a request to purchase gift cards. The provider’s reputation offers little insight into the request. However, limited communication history, suspicious language signals, and evidence of similar messages reaching other organizations could collectively support a malicious classification.

Now consider an employee sending a document from a personal account to a work address. That message also originates from a webmail provider, but its communication history and sender–recipient information may provide evidence of a legitimate interaction. WMC’s combination of features is designed to help distinguish such everyday exchanges from suspicious outreach.

Model Performance 

The model was trained on an internally curated and challenging dataset. By adding a mechanism to reduce False Positives (FPs), we were able to push the model’s precision in production to over 99%. The model has a “weighted” impact on the message’s trust score. High-confidence malicious classifications drop the score to the lowest range, while spam and lower-confidence classifications receive a milder negative score adjustment. This allows the system to distinguish the model’s assessment from the action supported by that assessment.

Source: Fortra
15

Oct

Privileged Access Management (PAM) helps small businesses control, monitor and secure access to sensitive systems, administrator accounts and business-critical applications. It reduces the risk of credential theft, excessive permissions and unauthorized access, without requiring a large IT or security team.

Small businesses are now one of the most targeted groups by cybercriminals. Attackers know that SMBs often run on lean IT teams, shared credentials and minimal oversight of who can access what. Keeper Security helps organizations of all sizes close that gap, starting with one of the most overlooked areas of security: PAM.

In enterprise environments, PAM has been a standard for years. However, for small businesses, PAM is just as critical and far less complicated to implement than most people assume.

The myth: “We are too small to be a target”

This is the most dangerous assumption in SMB security.

In reality, smaller organizations are often easier to compromise precisely because they rely on informal access habits: shared admin passwords, no offboarding process when employees leave and no audit trail of who accessed what and when. Learn more about how PAM is not only for large enterprises in our article.

The consequences of relying on shared credentials, weak offboarding processes and limited audit trails are serious. A single compromised admin account can give an attacker access to your entire network, customer data, financial systems and cloud services. For a small business, that kind of breach can be existential.

Common privileged access risks for small businesses

Most SMBs have the same blind spots when it comes to privileged access:

  • Shared credentials. When multiple people use the same admin login, organizations lose visibility into who did what, and revoking access when someone leaves becomes a manual, error-prone process.
  • No role-based access. Everyone gets more access than they need “just in case,” which significantly widens the attack surface.
  • No session monitoring. Without visibility into privileged sessions, organizations cannot detect unusual behavior until it is too late.
  • Weak offboarding. Former employees retaining access to critical systems is one of the most common sources of insider risk.

What privileged access management looks like for an SMB

As part of a broader cybersecurity strategy to help protect privileged access, here are some of the main PAM capabilities among the essential cybersecurity tools for SMBs:

  • A secure password vault that stores and auto-fills credentials, eliminating insecurely shared passwords
  • Role-Based Access Controls (RBAC) so each team member only accesses what their role requires
  • Audit logs that record who accessed what and when
  • Session monitoring and recording for high-risk connections like remote access or cloud admin panels

How SMBs can get started with PAM

The hardest part of implementing PAM for small businesses is often knowing where to begin. A practical starting point includes:

  1. Audit current access. List every system, tool and account with an admin or elevated login. Organizations will likely find more than expected.
  2. Identify shared credentials. Any password shared across multiple people presents an immediate risk. Replace shared credentials with individual, vaulted credentials stored in a password manager for small businesses.
  3. Apply least privilege. Review who has access to what, and remove permissions not required for an individual’s day-to-day role.
  4. Enable logging. Even basic audit logging provides visibility to help detect and respond to suspicious behavior.
  5. Automate offboarding. Make access revocation part of every employee departure process, rather than treating it as an afterthought.

How KeeperPAM supports small business deployment 

KeeperPAM combines a secure password vault, RBAC, session monitoring and recording and audit logging into a single platform built for organizations that need enterprise-grade protection without the enterprise complexity or cost.

One of the biggest misconceptions about PAM for small businesses is that it requires a large IT team or months of planning. KeeperPAM is designed to remove that barrier; Keeper’s onboarding specialists work alongside your organization from the start, helping you get up and running within hours or days.

Whether an organization is implementing PAM for the first time or replacing an existing solution, expert guidance is available at every step.

Privileged access management for small businesses is not a luxury or a future consideration. It is a foundational security layer that protects critical accounts from the attacks most likely to cause lasting damage. The right tools make PAM accessible to organizations of any size, without unnecessary complexity or heavy lifting.

Ready to take control of privileged access? Start a KeeperPAM free trial or request a demo to see how KeeperPAM works for your business.

Πηγή: Keeper Security

12

Oct

Keeper Security Surpasses 100,000 Enterprise Customers as Organizations Consolidate Identity Security Solutions in the Agentic Era.

Keeper Security, the leading zero-trust and zero-knowledge identity security platform, today announces it now protects more than 100,000 organizations globally. Keeper’s customer growth builds on consistent company milestones including surpassing $240 million in Annual Recurring Revenue (ARR) and also earning recognition from Gartner as the second fastest-growing competitor in the worldwide security software market in 2025. Adoption of Keeper’s identity security platform spans all industries, including finance, healthcare, telecommunications, manufacturing and the public sector, across more than 150 countries.

“This achievement is a testament to Keeper’s leadership in a market undergoing a paradigm shift, driven by the proliferation of AI in the enterprise,” said Darren Guccione, CEO and Co-founder of Keeper Security. “Forward-thinking security leaders are strategically moving beyond disparate, siloed software in favor of a unified identity control plane that offers unparalleled visibility, control and governance. They recognize that identity has become the primary attack surface, and platform consolidation is no longer just an option, but a strategic imperative. Keeper’s architecture was designed to address this complex reality, and our growth demonstrates that enterprises are decisively embracing this new direction.”

KeeperPAM consolidates password management, secrets governance, privileged session monitoring, endpoint privilege management, zero-trust network access and remote browser isolation into a single unified platform addressing the fragmentation that leaves most enterprises with visibility gaps across multiple tools. Unlike legacy identity security platforms, Keeper deploys in minutes without the complexity and cost barriers that slow enterprise adoption. The platform’s zero-knowledge architecture ensures that all credentials and session data remain encrypted with the customer’s private key, giving security teams complete control over their data.

Recent innovations driving enterprise adoption include KeeperAI, which delivers real-time session monitoring to reduce threat detection time by 99% with automated response across 100% of privileged sessions. To address the risks of autonomous agent deployment, Keeper extended agentic AI governance to Endpoint Privilege Manager, enforcing access policies, elevation controls and behavioral monitoring across both known and unknown AI agents. Concurrently, Keeper Secrets Manager integrates with Model Context Protocol (MCP) servers to secure credential access for AI agents, alongside certified enterprise connectors for platforms like Microsoft Azure Logic Apps to eliminate hardcoded secrets in automated workflows.

Platform adoption is further accelerated by deep ecosystem integrations. This includes an automated identity governance bridge with SailPoint that closes the gap between Identity Governance and Administration (IGA) and privileged access enforcement. Keeper’s integration with Wiz establishes Keeper as a remediation engine for identity security vulnerabilities discovered by the Cloud-Native Application Protection Platform (CNAPP). Additionally, Keeper has embedded privileged access and credential approvals directly into the communication and IT Service Management (ITSM) platforms organizations use every day – including Microsoft Teams, Google Chat, Slack, Jira, ServiceNow and Freshservice – enabling secure, zero-knowledge, just-in-time access requests and elevation approvals without requiring users to switch systems.

As the IAM landscape consolidates, Keeper stands as the unified identity and access platform for humans, machines and AI agents alike. For more information, visit keepersecurity.com.

Source: Keeper Security

8

Oct

Attackers using frontier AI models can now find vulnerabilities and generate exploits faster than organizations can patch them. And when malicious code is already running before an alert fires, detection alone is too late.

When attackers move at machine speed, defenses need to move just as fast. That’s what a prevention-first approach delivers: automatically blocking attacks before they execute.

We’re excited to announce that Sophos has been named a Leader in the IDC MarketScape: Worldwide Modern Endpoint Security for Enterprises 2026 Vendor Assessment (#US54123526, September 2026).
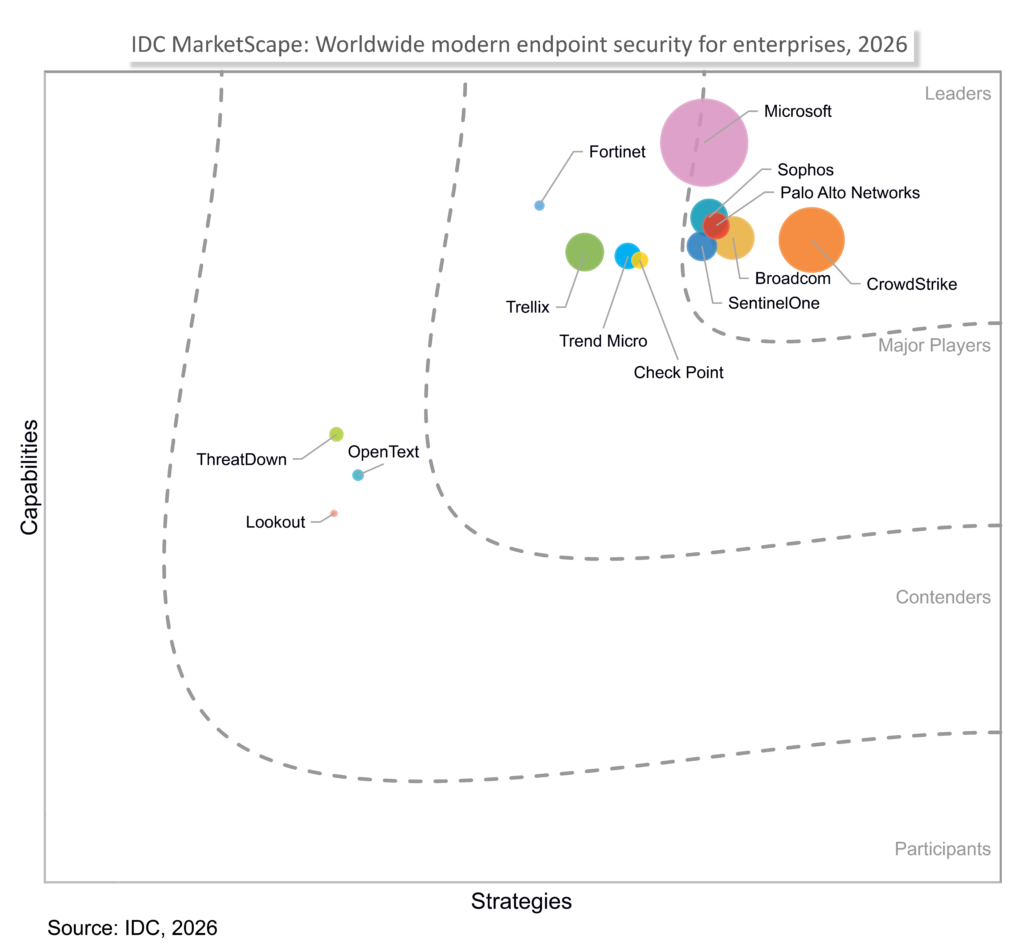
We believe this recognition reflects the strength of our prevention-first approach: stopping AI-era threats as early as possible while giving security teams powerful capabilities to detect, investigate, and respond.

According to the IDC MarketScape:

“Consider Sophos When: Organizations need a unified, open platform with strong third-party integration, native identity threat detection, and automation. SMBs to large enterprises are seeking out-of-the-box, protection-first endpoint security with minimal tuning.”

Prevention first, built for the AI era

AI gives attackers greater speed and scale, but successful attacks still depend on techniques that security controls can disrupt.

Sophos Endpoint is the strongest first line of defense against AI- and human-led attacks. A single lightweight agent combines AI-powered prevention, universal exploit prevention, ransomware protection, adaptive defenses, and built-in detection and response. Recommended protection technologies are enabled by default, with no configuration or tuning required.

Deep learning AI identifies known and previously unseen malware, including AI-generated and AI-mutated variants, before execution. More than 60 exploit mitigations, enabled by default on every process, block the exploit techniques that turn vulnerabilities into compromises. CryptoGuard monitors files for signs of malicious encryption by ransomware, blocks the offending process, and can automatically restore affected files.

The goal is straightforward: automatically prevent more threats from reaching the point where security teams need to investigate them.

Endpoint security connected through Sophos Fusion

Sophos Endpoint is part of Sophos Fusion, the Sophos AI-Native Cybersecurity Defense System. Endpoint telemetry flows into a unified context lake in real time, alongside signals from other Sophos controls and 500+ third-party integrations. Synchronized Security™ turns that shared context into coordinated action: detections are prioritized across layers, and a threat found at one control point triggers a response across the environment. Backed by Sophos X-Ops threat intelligence and real-world incident response insights, intelligence compounds across the 625,000+ organizations Sophos defends, so every threat seen anywhere strengthens the defenses of all customers.

With Sophos Fusion, security teams manage their Sophos products, review detections and alerts from Sophos and third-party security controls, investigate suspicious activity, and remediate threats.

We believe Sophos’ recognition as a Leader in the IDC MarketScape: Worldwide Modern Endpoint Security for Enterprises 2026 Vendor Assessment reinforces the strength of this approach and our focus on helping organizations stop threats before they become business-disrupting events.

Learn more

Read the IDC MarketScape excerpt.

Learn more about how Sophos Endpoint delivers prevention-first, AI-powered endpoint security designed to stop attacks earlier, reduce operational complexity, and help security teams investigate and respond faster.

Source: Sophos
6

Oct

What is Sophos CISO Advantage?

Organizations have heavily invested in threat protection, but many still cannot say whether it is working, where their biggest risks are, or what to address next.

Part of the challenge is that few have the strategic in-house resources they need to do so. Only around 1 in 10,000 organizations has a dedicated CISO, leaving the vast majority without the strategic oversight needed to measure, improve, and demonstrate their cybersecurity posture. 79% of organizations are also struggling to keep pace with changing compliance requirements, with IT and security teams spending 39% of their time on compliance-related activities.

Sophos CISO Advantage helps solve these challenges. It gives organizations validated, framework-mapped evidence of whether their controls are working, a prioritized, budget-aligned roadmap for what to fix first, and board-ready reporting that translates security data into business insight. The result is evidence that holds up with a board, an auditor, or an insurer.

Sophos CISO Advantage is delivered through Sophos Fusion, the industry’s most complete cyber defense system. Enabled by the Sophos AI-Native Cybersecurity Defense System architecture and 500+ Sophos and third-party integrations, it sees everything, connects everything, and enables your defenses to respond as one. Powered by agentic AI, with human judgment, Sophos Fusion protects organizations from AI-enabled threats that move at AI speed.

Who is Sophos CISO Advantage for?

IT stakeholders, security leaders, and security teams 

Sophos CISO Advantage helps organizations understand and manage cyber risk, while giving them the structure to continuously track their cybersecurity posture, streamline compliance, and align performance with future decision making.

For teams without a dedicated CISO, it provides a central source of truth, helping them keep pace with changing requirements and understand what to address next.

For organizations with a CISO, it reduces the tactical burden of gathering data, interpreting findings, and producing reports, enabling those leaders to focus on what they were hired to do — guiding the organization’s security strategy.

For all organizations, Sophos CISO Advantage helps them build and lead a strategic, measurable cybersecurity and compliance program by:

  • Accelerating assessments and uncovering deeper insights with AI-enabled workflows that reduce manual effort and give teams their time back
  • Delivering the right information to every stakeholder with tailored reporting for technical teams, executives, and the board
  • Benchmarking security performance and maturity against industry peers to provide context and strategic direction
  • Turning findings into action with gap analysis and prioritized recommendations that guide investment and resource allocation

Together, these capabilities move organizations from asking, “Where are we?” to having a clear answer: “This is what we should do next.”

MSPs and service providers

For MSPs and other channel partners acting as CISO for their own customer base, Sophos CISO Advantage helps transform that role into a structured billable service so they can respond to increasing demand for strategy and continuous compliance while deepening customer relationships. Find out more here.

Source: Sophos

1

Oct

Sophos Firewall v23 brings many of your top-requested enhancements in one feature-packed release.

From new AI-powered assistance and a modern REST API to streamlined rule management, stronger high-availability capabilities, expanded identity support, and simpler day-to-day administration, Sophos Firewall v23 is designed to make your firewall easier to manage, automate, and scale, while further strengthening its Secure by Design foundation.
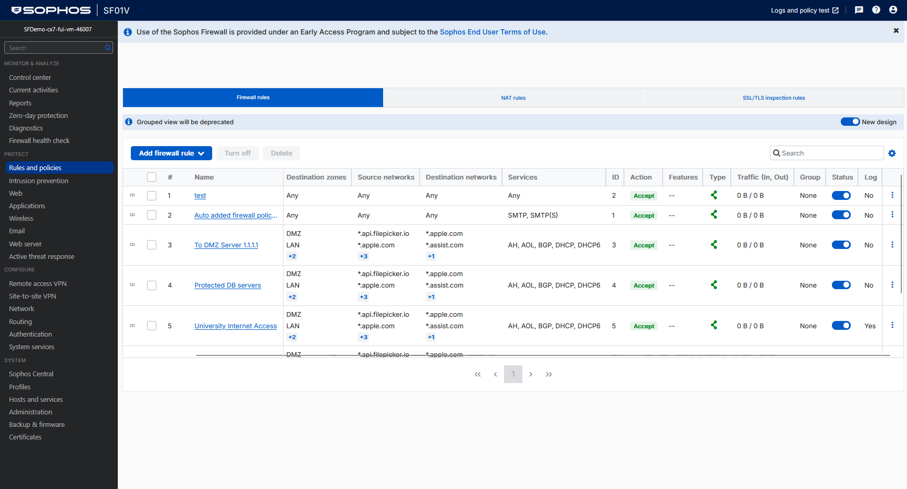
The new firewall rule management screen is just one of your many top-requested enhancements in Sophos Firewall v23
While there are dozens of enhancements across all areas of the firewall, the highlights fall into five key areas:

AI and automation

With Sophos Firewall v23 and Sophos AI Defense, you gain better visibility into AI usage across your organization and can easily implement appropriate controls, while the new API enables you to automate firewall management. Also be sure to take advantage of the new AI assistant to help with constructing firewall rules.

What’s new:

  • Enhanced AI governance and visibility support through Sophos AI Defense
  • Modern REST API with token-based authentication with built-in API guide
  • AI-powered Firewall Assistant in Sophos Fusion

Simplified management and greater resilience

Sophos Firewall v23 makes day-to-day administration easier and helps keep your network running smoothly, even under demanding conditions. Whether you’re managing a single firewall or hundreds, you’ll benefit from a redesigned rule management experience, improved visibility, faster performance, and significant enhancements to high availability.

What’s new:

  • Completely redesigned firewall rule management experience
  • Hardware-aware high availability monitoring and faster failover detection
  • Improved HA stability under heavy load
  • Automated firmware update scheduling in Sophos Fusion
  • Faster and more responsive administration interface
  • Improved navigation and firewall status visibility for administrators

Secure by Design enhancements

Sophos Firewall continues to build on its strong Secure by Design foundation with enhancements that further reduce your attack surface, improve security visibility, and simplify protection. New capabilities help secure DNS traffic, provide greater transparency into automated security updates, and make it easier to stay protected with the latest firmware and platform improvements.

What’s new:

  • DNS over HTTPS (DoH) support for stronger DNS security
  • Support for DNSSEC to authenticate DNS responses
  • Visibility into applied hotfixes and security updates
  • Modernized routing architecture and management
  • Improved threat response event handling
  • Additional platform hardening and security enhancements

Modern identity and access integration

As organizations continue to adopt cloud and hybrid identity services, Sophos Firewall v23 expands integration options and simplifies authentication. You can more easily connect users across on-premises and cloud environments while improving MFA onboarding and extending support to a wider range of devices and deployment scenarios.

What’s new:

  • Entra ID support for Synchronized Security
  • Google Workspace identity provider integration
  • More secure MFA onboarding via email
  • Chromebook single sign-on support
  • Enhanced support for terminal servers and shared-user environments

Scalability, networking, and application protection

Sophos Firewall v23 includes a wide range of infrastructure and networking enhancements designed to help support your growing environment. From major Web Application Firewall enhancements and a redesigned DHCP service to expanded IPv6 support and improved service discovery, v23 delivers better scalability, performance, and flexibility.

What’s new:

  • Major Web Application Firewall performance and scalability improvements
  • Expanded WAF rule capacity and routing capabilities
  • New DHCP service architecture
  • mDNS reflector for education, campus, and segmented network environments
  • Enhanced IPv6 and IPoE connectivity support
  • Additional cloud platform deployment options

Summary

Sophos Firewall v23 delivers 30 of your most-requested enhancements, helping you to manage and secure your network more effectively. It makes Sophos Firewall easier to manage while continuing to strengthen its Secure by Design advantage. Whether you’re managing a single firewall or a large distributed deployment, you’ll benefit from improvements that save time, simplify administration, and strengthen protection.

More details

Review the What’s New Guide for more details.

Get started today

You can download the upgrade package or installer for v23 from the Sophos Firewall v23 EAP Registration Page. Simply submit your details and the download links will be emailed to you straight away.

All support during the EAP will be through our forums on the Sophos Firewall Community.
 

Source: Sophos
29

Sep

Every few weeks, the AI conversation seems to reset around a new warning.

A model demonstrates an unexpected capability. An autonomous agent behaves in a way its designers did not anticipate. A new forecast describes how quickly AI could transform work, security or society. The details change, but the pattern is familiar: a new development emerges, the debate swings between extraordinary promise and existential danger, and organizations are left wondering whether their strategy must change again.

There is a legitimate case for stronger testing, greater transparency, independent evaluation, and guardrails that keep capability advances from moving too far ahead of our ability to secure them. Innovation without accountability is not a sustainable strategy.

But neither is waiting for the AI debate to be resolved.

For security leaders, the central question is not whether every forecast about AI will prove correct. It is whether their organizations can adapt safely as the technology, the threat landscape and the way people work continue to change.

That has always been the job.

The stakes are also not shared evenly. The cybersecurity poverty line existed well before AI but, since it significantly raises the cost of both attack and defense, the organizations most exposed are often the ones that were already under-resourced.

Adaptability is not the same as overreaction

Security leaders need to resist two equally dangerous impulses:

  • The first is complacency: assuming today’s controls will remain sufficient simply because the fundamental principles have not changed
  • The second is overreaction: allowing every new AI development to trigger a wholesale reinvention of strategy.

Neither approach builds resilience.

Instead, the focus should be on adaptability; that is, preserving a stable security foundation while changing how that foundation is applied. This is especially important because the AI news cycle is unlikely to slow down. There will be more incidents, more capability demonstrations and more disagreement about what they mean. Security leaders cannot operate effectively if their attention and investments move in lockstep with every headline.

They need a durable way to decide what matters.

A useful starting point is to focus less on whether an AI tool appears novel and more on what it can access, what it is authorized to do, and what the consequences would be if it behaved unexpectedly.

This is where risk-based governance becomes essential. Organizations should be able to experiment, but the strength of the control should rise with the autonomy, access, and potential impact of the use case.

That principle allows innovation to continue without pretending every application of AI carries the same risk.

We need guardrails that strengthen innovation

Calls for caution are sometimes interpreted as calls to stop. Calls for innovation are sometimes interpreted as opposition to oversight. That is a false choice, largely because AI is dual use. The same advances that can help defenders analyze activity, investigate threats, and respond more quickly can also help adversaries operate at greater speed.

The question is not whether guardrails are needed; they are.

The better questions are whether those guardrails are proportionate, verifiable, and focused on measurable risk. Regulation should establish accountability, improve transparency, and make it harder for dangerous capabilities to be developed or deployed without appropriate scrutiny.

However, regulation should not freeze responsible innovation or make advanced defensive capabilities accessible only to the organizations with the greatest resources.

Rules that unintentionally slow defenders, restrict responsible research or raise the cost of protection could widen the gap between organizations that can defend themselves and those that cannot.

Instead, the goal should be to create a race to stronger security, which requires close collaboration. Frontier AI developers understand their models. Cybersecurity experts understand how systems are attacked, where operational controls fail and how risk appears in real environments. Policymakers can establish accountability and defend the public interest.

None of those groups can solve the problem alone.

The security work in front of us already exists

Much of the public debate is focused on what the next generation of AI might be able to do. Security leaders do not have the luxury of concentrating only on a future model.

The technology available today is already changing how people create, communicate, analyze information and make decisions. AI tools and agents are already entering organizations, sometimes through approved programs and sometimes without the knowledge of IT or security teams.

Even if frontier AI development stopped today, that work would remain.

Organizations would still need to discover unsanctioned AI use. They would still need to understand which information is being shared with external services. They would still need to assess integrations, permissions and identities. They would still need to monitor for abuse and prepare for mistakes. They would still need to help employees use AI productively without creating unacceptable risk.

That is why a slowdown cannot be the security strategy.

The strategy must be to build organizations that can adopt technology safely, respond to change, and maintain control even when the direction of innovation remains uncertain

The fundamentals should not change every time the narrative does

Cybersecurity has never operated in a stable environment. Threat actors evolve, technology architectures shift, geopolitical events alter risk, and new applications appear inside organizations before security teams have had time to assess them. That’s just part of the day-to-day.

AI raises the speed and scale of that change, but it does not eliminate the foundations of sound security. Organizations still need to know what is in their environment, understand who and what has access to sensitive systems and data, and controls that limit exposure, detect malicious activity, and support an effective response when a threat is identified.

In other words, priorities may move, but the fundamentals must hold.

We saw a similar dynamic during the transition to the cloud. Nobody secured the cloud by treating every new application as a separate strategic crisis. We adapted our security models by developing new forms of visibility, establishing new controls, and learning how to manage a technology environment that would continue to evolve.

AI requires the same discipline, but with an important difference. Unlike previous technology evolutions, AI adoption does not arrive through a centrally managed transformation program. It can enter an organization one employee, one browser tab, one application integration, or one autonomous agent at a time.

That makes adaptability inseparable from visibility. Security teams cannot assess risk, apply appropriate controls, or govern AI usage if they do not know where and how AI is being used across the business.

Making secure AI adoption accessible

At Sophos, our mission has long been to help close the cybersecurity poverty line. That mission matters even more in the AI era.

Our role is to help customers safely adopt the tools they choose while bringing the strongest available security technology within practical reach. That means giving organizations visibility across their environments, helping them identify risk, and applying protection in ways that match their operational reality.

It also means working closely with the organizations building frontier AI systems. AI developers can accelerate safely when they build alongside cybersecurity specialists who see how threat actors behave in the field and how technology is used in real organizations.

This is not an argument for moving fast and ignoring the consequences. Rather, it is an argument for making security part of innovation from the beginning.

The fundamentals are available to us now: know what is operating in your environment, understand what it can access, apply controls according to risk, monitor what it does, and prepare for failure. Above all, adapt as the evidence changes.

AI may move faster than any technology transition that came before it. That does not mean security strategy must move with every headline. It simply means the strategy must be built to adapt.

Source: Sophos

25

Sep

Security information and event management (SIEM) has come a long way since its inception over 20 years ago. Adoption was originally driven by The Payment Card Industry Data Security Standard (PCI DSS) but has since enjoyed widespread use due to its joined-up approach to identifying and combatting security threats.

Just monitoring one system in isolation isn’t suitable for modern-day security. According to the Global Incident Response Report by Palo Alto Networks, 87% of intrusions involve activity across multiple attack surfaces, including endpoints, networks, cloud, SaaS and identity.

So, it’s no surprise that SIEM has caught the eye of legislators, with the NIS2 directive (which covers many companies in the EU, and indirectly their supply chains) giving guidance that specifically recommends SIEM to aid compliance.

Here are five ways Kaseya SIEM helps organisations with NIS2 compliance.

1.SIEM helps identify security incidents faster

One of NIS2’s central requirements is the ability to detect, monitor and respond to cybersecurity incidents effectively. This is all about bringing together the data from across your organisation to detect potential threats and respond to them.

Guidance states that the ability to correlate information between systems is important for compliance. It also suggests SIEM as an evidence point for the monitoring and logging portion of incident handling.

Without this orchestration ability, you are looking at individual signals in isolation. SIEM is what brings them together to provide a unified picture of threats to your organisation.

2.SIEM provides the context needed for incident response

Detecting an incident is only the first step.

Organisations must also determine the severity of the threat, understand its potential impact and decide how to respond.

Is it a small security issue that can be fixed quickly and without further intervention?  Or is the incident severe enough to trigger other parts of your security planning?

You can’t decide it in the moment. That pathway must be laid out clearly in advance. NIS2 guidance suggests ensuring you have clear criteria on what can be classed as an incident, how the severity is categorised and how you then handle it as a result.

But the SIEM data — and understanding the severity of the incident — is what provides that foundation of information that allows you to trigger the appropriate response.

3.Automation accelerates response times

Responding to an incident quickly could be the difference between nipping an issue in the bud versus that issue grinding your business to a halt. According to the CrowdStrike Global Threat Report 2025, it takes just 48 minutes on average for attackers to move laterally from initial compromise.

As part of incident response, NIS2 guidance suggests the use of automated solutions. Automation across cloud, email and endpoint can trigger an immediate response before an engineer even receives the notification.

Kaseya SIEM’s automated response rules stop threats without manual intervention. In fact, you can use automated response rules out of the box, or fine tune and create your own.

4.Tailored security helps you focus your efforts

Acknowledging the sheer wealth of data that could overwhelm a team, NIS2 guidance suggests utilising automation to triage incoming alerts and prioritise them based on severity.

NIS2 recognizes the importance of focusing resources on genuine risks and minimizing false positives wherever possible.

Kaseya SIEM allows you to define your own custom indicators of compromise and adjust alert severity. When combined with automated response, it allows you to tailor responses to fit your environment and ensure that your teams respond to what matters most.

5.Logs give the evidence you need after an incident

There is no set way an investigation may unfold, or indeed what may trigger one. But, if auditors do carry out an investigation after a security breach, having the right data on hand is vital.

Auditors will likely want to see how you handled the incident, the data used to inform your resolution and the steps you took. They may also want to see what data you were collecting and how you were interpreting and acting upon that data before the event.

With a 400-day log retention, Kaseya SIEM has that covered. And when you consider it takes an average of 241 days to identify and contain a breach, that length of log retention becomes even more important.

There’s SIEM -and then there’s Kaseya SIEM

Kaseya has taken SIEM and adapted it for modern threats. While SIEM has always been a powerful tool for aggregating data, Kaseya SIEM combines AI automation along with a high level of customisation so you can tailor and speed up your response to an incident.

The cost of not having a SIEM solution could also have wider ramifications. Many cyber insurers now require SIEM or SOC coverage as a condition of policy renewal. Kaseya SIEM offers both.

In addition to the automated responses and tailored alerting, Kaseya SIEM is also backed by a 24/7 SOC that scans for issues at all times.

NIS2 calls for the right tools with the right people and the right training — and by combining SIEM with SOC, Kaseya SIEM helps organisations tackle both parts of the requirement.

Find out more about Kaseya SIEM.

Source: Kaseya

22

Sep

For years, the cybersecurity industry has blurred the lines between XDR and SIEM. As capabilities converged, organizations were left trying to connect separate security operations and compliance solutions, often moving the same data between different tools, workflows, and teams.

Security teams have been asked to do more than ever: detect and investigate threats faster, automate response actions, and retain growing volumes of data. This is in addition to reconstructing activity across different systems, manually correlating events, and bridging gaps between operational and compliance requirements.

Pricing tied directly to data ingestion created another challenge. As data volumes grew, organizations were forced to choose between greater visibility, retention, and cost, even when historical context could prove critical during an investigation, audit, or incident review.

At Sophos, we think the conversation has focused on the wrong thing.

The question is not whether an organization needs XDR or SIEM. The question is whether security operations and compliance should require separate solutions, separate workflows, and separate data foundations in the first place.

We don’t think so. The work is different. The data does not have to be.

Designed around outcomes, built on shared context

When Sophos acquired Secureworks in 2025, we brought together two of the most influential lineages in cybersecurity. This gave us an opportunity to rethink how security operations and compliance should work together.

Rather than forcing organizations to treat XDR and SIEM as separate data foundations, Sophos Fusion brings them together through shared context while keeping security outcomes at the center.

Within Sophos Fusion, the industry’s most complete cyber defense system, telemetry from Sophos and third-party  control points flows into a unified context lake. Security operations capabilities use that context to detect threats, investigate activity, automate workflows, and accelerate response. Compliance capabilities draw from the same foundation to support long-term data retention, reporting, and evidentiary needs.

Distinct outcomes. Shared context. One cyber defense system.

Security remains the focus

Organizations should not have to add a separate SIEM to access the capabilities required for effective security operations.

Sophos XDR Powered by Secureworks delivers the capabilities analysts need to detect, investigate, and respond. AI-assisted detection analysis and natural-language search help teams understand activity faster. Context-rich cases bring together related evidence and threat intelligence. Built-in automation, SOAR workflows, response actions, and over 500+ third-party integrations help analysts move from detection to containment without manually assembling response across disconnected tools.

These capabilities belong in XDR because they directly contribute to security outcomes. Compliance builds on that security foundation rather than competing with it.

Sophos Next-Gen SIEM helps organizations retain, report, and prove. Flexible data ingestion and AI-assisted parsers bring in telemetry unique, legacy, regional, and internally developed sources. Retained data remains structured and searchable, supporting compliance reporting while adding historical context to the security operations already taking place in Sophos XDR or Sophos MDR.

Pricing based on users and servers rather than data volume helps organizations retain the data they need without turning every increase in visibility into an increase in cost. This means fewer trade-offs between security, compliance, and budget, with historical context available when analysts, auditors, or incident responders need it.

A clearer path forward

The cybersecurity industry spent years blurring the lines between XDR and SIEM. Organizations were left trying to determine whether they needed one solution, the other, or both.

Sophos is taking a different approach.

Within Sophos Fusion, Sophos XDR and Sophos Next-Gen SIEM are designed around the outcomes organizations need, not the boundaries between product categories. Security teams can detect, investigate, and respond. Compliance teams can retain, report, and prove. Both work from the same foundation of data and context, within a single cyber defense system.

Sophos XDR Powered by Secureworks and Sophos Next-Gen SIEM are now generally available as part of Sophos Fusion. Existing Sophos XDR and Sophos MDR customers can add Sophos Next-Gen SIEM to their environment. New customers can adopt Sophos XDR with Next-Gen SIEM, or pair Next-Gen SIEM with Sophos MDR for fully managed, 24/7 detection and response supported by extended historical context.

Whether you’re looking to strengthen security operations, simplify compliance, or bring both together through shared context, visit Sophos.com/NG-SIEM or contact your Sophos representative to learn more.

Source: Sophos

18

Sep

GigaOm has recognized Keeper Security in the Enduring Innovators quadrant of its 2026 Radar Report for Enterprise Password Management. This marks the fifth consecutive year that Keeper has been named a Leader in GigaOm’s evaluation of the enterprise password management market.

The report recognizes Keeper’s continued innovation, architectural depth and ability to help organizations secure more than just passwords. With Keeper, enterprises can protect credentials, secrets, machines, non-human identities and AI agents from a single, unified platform. Request a demo today to see firsthand why we are ranked so highly.

Report overview and key highlights

GigaOm’s 2026 Radar Report examines 23 leading enterprise password management solutions. It evaluates each provider against a range of capabilities, including table-stakes, key and emerging features, as well as broader business criteria.

The Enduring Innovators quadrant recognizes platforms that continue to build on their market position through ongoing innovation and strong underlying architecture. Keeper was recognized as advancing faster than the majority of the field, with particular strengths in secrets management, its official Model Context Protocol (MCP) server and governance for agentic and non-human identities.

This is the fifth year that GigaOm has evaluated the enterprise password management market  and the fifth consecutive year that Keeper has earned a Leader designation.

How Keeper stands out 

Unlike fragmented tools or limited vault-only solutions, Keeper provides a zero-trust, zero-knowledge security architecture for protecting credentials and access across the enterprise. Key strengths include:

  • Compliance-ready security: FedRAMP High Certified and GovRAMP High Authorized, FIPS 140-3 validated, with longstanding SOC 2 and ISO certifications.
  • One platform for every identity: Govern human, machine, non-human and AI agent identities from a single control plane.
  • Built-in secrets management: Protect credentials used by developers, applications, services and infrastructure.
  • Secure access anywhere: Use Keeper across desktops, mobile devices and browsers.
  • Fine-grained controls: Apply least-privilege principles with time-limited access, one-time sharing and self-destructing records.
  • Broad integrations: Connect with SSO, MFA, SIEM, CI/CD tools and passwordless authentication.
  • Fast deployment: Deploy in minutes alongside existing tools, no disruptive rip-and-replace required.

Innovation since the last GigaOm report

The identity security landscape is changing quickly, with AI agents, machine identities and non-human accounts becoming part of everyday business operations. Keeper has responded by continuously expanding its platform to help organizations manage these identities alongside their workforce.

The latest capabilities include AI agent governance, an official MCP server, real-time threat detection through KeeperAI, improved risk visibility and stronger session protection. Keeper has also expanded passkey and passwordless authentication, while KeeperPAM brings password management, secrets management, privileged access management and endpoint privilege management together in one unified identity security platform.

Together, these updates give security teams greater visibility and control as identity environments become more complex. To see the full Keeper platform beyond just password management, request a demo of KeeperPAM.
Why enterprise password management matters

Weak, reused or exposed credentials can leave organizations vulnerable. Enterprise password management helps security teams protect passwords, secrets and machine credentials while enforcing access policies, supporting passwordless authentication and maintaining clear audit trails.

Password management is about more than just storing passwords. It provides centralized control and visibility across users, devices, applications and identities.

Try Keeper for free

Protect your organization’s passwords, credentials and secrets with zero-trust and zero-knowledge security. Sign up for a free 14-day trial or reach out to our team to learn more.

Looking to secure your organization beyond password management? Learn more about KeeperPAM®

Strengthen your organization’s security posture by investing in a privileged access management solution that supports a zero-trust strategy. KeeperPAM is both zero trust and zero knowledge, which helps prevent unauthorized access and ensures that only the right users have the appropriate level of access. With features like endpoint privilege management, role-based access control, Just-in-Time (JIT) access and detailed auditing, monitoring and session recording, KeeperPAM helps your organization secure critical data and maintain tight controls over all infrastructure.

To learn more about how KeeperPAM can secure your organization with its zero-trust strategy, request a demo today.

Source: Keeper
15

Sep

A question every business should be asking is: How quickly can we get back to business if something goes wrong?

Downtime is expensive, and in extreme cases, can even affect the wider economy — with the Jaguar Land Rover cyberattack estimated to have wiped out 0.1% of the UK’s GDP.

That’s why legislation such as the EU NIS2 Directive places a strong emphasis on recovery capability, not just prevention, for companies deemed “critical” or “important.” Even organizations that are not directly subject to NIS2 may still need to demonstrate appropriate safeguards if they want to do business with customers, partners or suppliers that are.

But every company should be asking this question, whether they are affected by the legislation or not. Backup is no longer simply about having another copy of your data. It’s a key part of any disaster response and how quickly you can move from recovery to normal business operations.

That’s why backup and recovery discussions are moving beyond IT departments and becoming board-level priorities.

How a good backup strategy supports NIS2

For many years, the widely accepted backup framework was:

  • 3 copies of data (to protect against data loss)
  • 2 different formats (stored on at least two media types)
  • 1 off-site copy (to protect against physical disasters)

However, it’s now recommended to add two more measures for true backup efficacy:

  • 1 immutable copy (ensuring ransomware-proof backups)
  • 0 doubt you can recover (regular testing guarantees reliability)

This evolving approach has a key part to play in NIS2 compliance.

What does NIS2 say about backup strategy?

At NIS2’s core is a focus on recovery and business continuity. It’s about ensuring disruption is kept to a minimum in the event of an incident. As such, most sections of NIS2 legislation are supported by a good backup strategy.

Three areas are particularly relevant.

One of the pillars of NIS2 is “policies to assess effectiveness.” Put simply, this isn’t just about the belief you have effective backup in place — it’s the ability to prove you do.

A backup is useless if you can’t use it. The “0 doubt you can recover” principle should form part of any recovery strategy,  supported by documented recovery procedures and regular testing. Organizations need confidence that when recovery is required, it will work as expected.

Meanwhile, the immutable copy addresses the legislation’s need for “business continuity measures” and basic “computer hygiene.” It’s vital to have a copy of data that cannot be altered or deleted and can act as a known and reliable restore point if needed. This is necessary for general disaster recovery and offers a reliable version of data in the event of a cyberattack or ransomware incident.

Avoid cloud complacency

One of the biggest misconceptions in modern IT is the assumption that cloud services automatically provide complete protection, and that providers will handle backup and recovery. The problem is exacerbated by SaaS, where the promise of instant access to a solution is enticing and often achieved without IT involvement.

Even well-established services like Microsoft 365 can have backup blind spots if organizations do not have an independent protection strategy in place

The term “cloud blindness” has been coined for this and other areas of cloud complacency.

While cloud services may bake in a certain amount of resiliency, businesses cannot take a hands-off approach to critical areas such as backup and recovery.

Businesses need to employ a zero-trust policy when it comes to their data integrity. Regardless of who has stored the data or where, and regardless of the promises given in terms of reliability, the backup strategy must remain consistent across the board.

Backups are about getting back to business

In a world where ransomware attacks are increasingly common and SaaS outages are frequently making headlines, backups need to be a key part of any compliance posture.

Every moment of downtime is potentially lost revenue. The legislation’s approach to making IT part of boardroom governance is good for IT teams, and Datto has long been making the case for backups to be an important part of this discussion.

Read Datto’s The ultimate guide to BCDR: Why backup and disaster recovery matter.

Source: Kaseya

12

Sep

Privileged accounts are standing invitations for attackers, with credentials to steal and permissions to misuse. When administrative rights are persistently active, whether or not they’re being used, privileged accounts significantly expand the attack surface. Zero Standing Privilege (ZSP) shrinks that risk by ensuring no user holds permanent elevated access. Instead, privileges are requested for a specific task, granted for a limited time, approved through a defined workflow and automatically revoked when the approved window expires. ZSP reflects a broader shift in modern security, replacing standing access with temporary access to reduce what an attacker can exploit. Keeper helps enforce ZSP by granting Just-in-Time (JIT) access and automatically revoking it when the approved window expires, moving users from zero privilege to exactly the access they need, then back to zero automatically.

Continue reading to learn the importance of ZSP, how it works in Keeper and where Keeper enforces it across environments.

Why standing privileges are a security risk

A privileged account that stays active indefinitely gives attackers a long-lasting target: the credentials don’t expire, the access is constantly available and there’s no given moment when those rights are taken away. If attackers steal or compromise one of these accounts, they inherit standing privileges in their entirety.

The bigger problem is blast radius since a compromised account with standing access rarely stops at the system for which it was intended. Attackers use standing privileges to move laterally across environments, reaching additional servers, databases and cloud resources in their paths. What may begin as a single compromised credential can quickly turn into a foothold across your entire infrastructure if the user has standing access. When privileges are permanent, access isn’t tied to a specific request, task or timeframe, leaving no clear record of why someone could reach a system at a certain moment. That ambiguity makes investigating security incidents involving standing privileges and proving compliance much more challenging.

How zero standing privilege works in Keeper

Keeper helps enforce ZSP through Keeper Privileged Cloud, which extends KeeperPAM’s JIT access framework to your identity providers and federated applications. Instead of provisioning permanent admin rights, Keeper Privileged Cloud grants elevated access only when it’s requested, only for an approved time window and only under the workflow controls you define. Users default to no privilege and elevate through a controlled, auditable process, then return to zero when the task is done. Below is how ZSP works in practice for Keeper.

Configure access policies

On a PAM Cloud record, admins define the rules of engagement using JIT and Workflow settings. This includes whether a request needs approval, who can approve it, how long access lasts once granted and which role the user is elevated into. These settings help determine exactly how privileged access is requested, approved and time-boxed, ensuring no elevation happens beyond the boundaries you set.
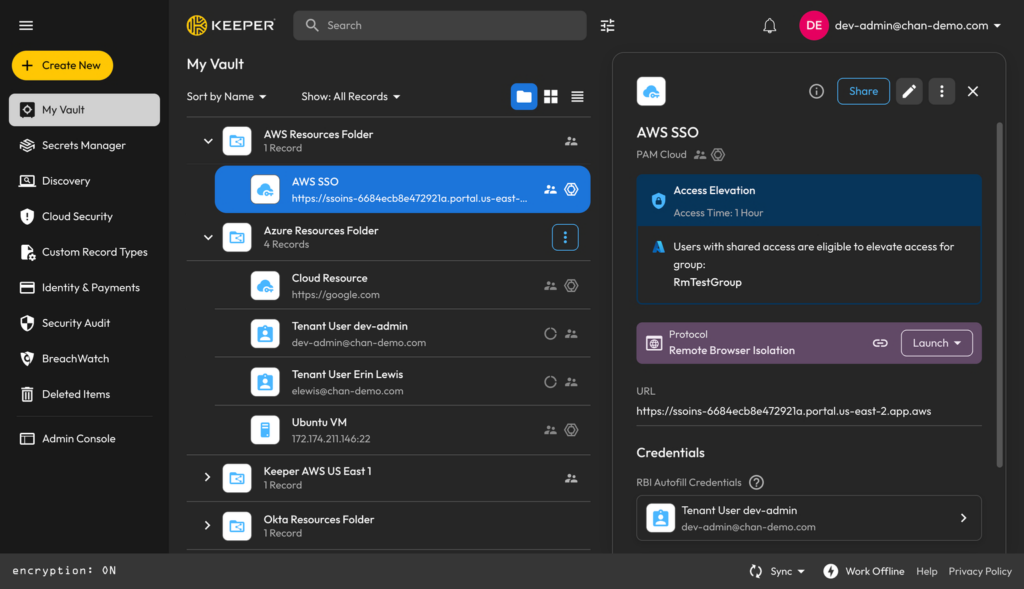
Share records with authorized users

Once a policy is in place, the PAM Cloud record is shared with the users who should be able to request access. Because elevation happens through your identity provider, each user needs an account in both your identity provider and Keeper tenant. With the record shared, those users can request elevated access when a task calls for it, without holding any standing privilege in the meantime.

Review and approve requests

When a user needs access, they can request it directly from their Keeper Vault or the Keeper Commander CLI. Designated approvers receive real-time notifications from tools like Slack, Teams, Jira and ServiceNow and can either approve or deny a request from any Keeper client, so requests aren’t stuck waiting for someone to be at their desk. Depending on the policy, approvers can also require a justification and a ticket number before granting access, linking every elevation to a documented reason.
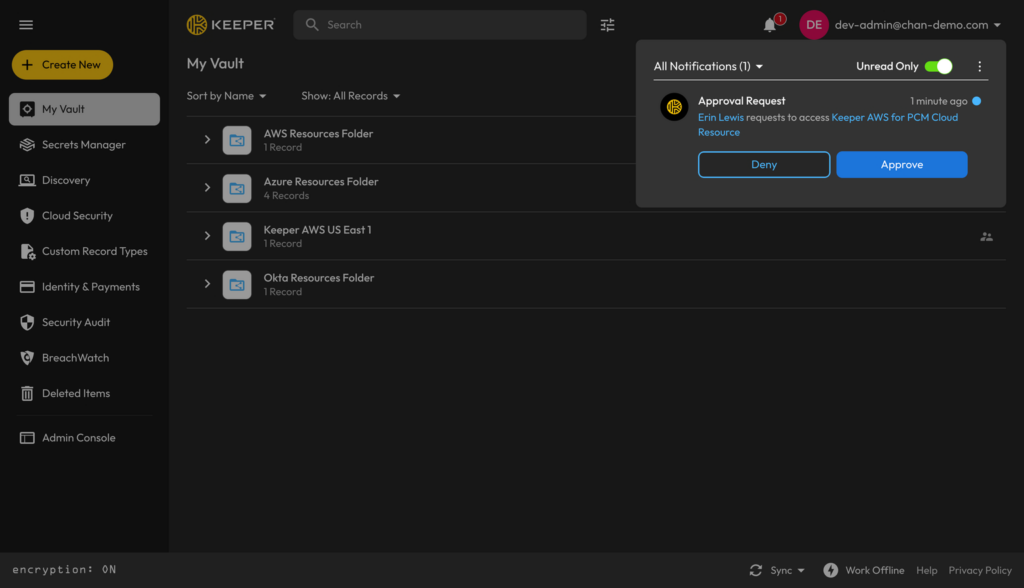
Grant and revoke access automatically

After a request is approved, the Keeper Gateway performs the elevation on the identity provider or target resource, granting the user the configured group membership, role or entitlement so they gain the access the policy allows. When the approved duration expires, the Keeper Gateway automatically revokes that access, removing the temporary membership or assignment and returning the user to ZSP. It also records every elevation that requested access, who approved it, and when it started and ended so security and compliance teams have a clear, per-request account of how privileged access was granted and used.

Where Keeper enforces zero standing privilege

Keeper doesn’t confine ZSP to a single system or account type. The same JIT framework applies wherever privileged access exists in your environment, from the identity providers your users authenticate against to the cloud resources, databases and machines behind them.

Across your identity providers

Keeper Privileged Cloud extends JIT access across existing identity providers, including AWS IAM, Microsoft Entra ID, Google Cloud via Google Identity, Okta and Active Directory. Keeper grants and revokes privileges directly within your existing infrastructure, so elevation happens where your accounts already live with no disruption to how users authenticate. The identity provider remains your source of truth, while Keeper simply controls when a user is elevated into a privileged group and when they’re removed from it.

That reach is not only for the platforms themselves but also includes applications that federate access and authorization through these identity providers. Federated applications can also use Keeper for access control, allowing users to apply the same JIT model to the downstream apps that teams sign into every day.

Across cloud, databases and machines

Since ZSP isn’t just a cloud-console issue, KeeperPAM applies the same privilege-elevation framework beyond your identity providers. Using PAM Cloud, PAM Database and PAM Machine records, you can extend time-limited access to cloud resources, databases and individual machines, bringing the same lifecycle to the infrastructure behind your identity layer.

Beyond elevation, the Keeper Gateway also rotates privileged credentials so they don’t linger as static targets, and for databases and machines it can provision ephemeral accounts, injecting credentials server-side so the user never handles them. All of it sits within Keeper’s zero-knowledge architecture, meaning credentials and secrets remain end-to-end encrypted and are never exposed to Keeper or anyone else. Together, automated rotation and zero knowledge ensure that even the credentials that enable privileged access don’t persist as materials an attacker could steal and exploit.

Minimize your attack surface with Keeper

Zero standing privilege only works if it’s enforced consistently, which is where Keeper Privileged Cloud thrives. With Keeper, security teams have an auditable way to grant privileged access on demand and revoke it automatically, working through the identity providers and infrastructure you already run. Administrators get provable control over who can access what and when; users get the access they need without waiting for manual provisioning or holding on to rights they don’t.

Request a demo of KeeperPAM to see JIT access and automatic revocation in your environment.

Πηγή: Keeper